Secure Your Software Supply Chain with Checkmarx Ecosystem Solutions
Overview
Checkmarx One is an enterprise application security platform that helps organizations secure source code, open-source dependencies, containers, and cloud-native applications throughout the software development lifecycle. By combining application security testing with developer-friendly workflows, Checkmarx enables teams to identify vulnerabilities early, prioritize risk, and deliver secure software without slowing development.
Key Products
Checkmarx One
A cloud-native central hub that combines all your scan results into a single view, letting you track security compliance and risk trends across your entire codebase.
Checkmarx One Assist
An AI security companion that works right inside your code editor to explain security issues and provide merge-ready code fixes you can accept instantly.
Checkmarx NG SAST
A high-speed code scanning engine that analyzes your proprietary source code for hidden flaws and vulnerabilities while minimizing frustrating false alarms.
Checkmarx Software Supply Chain Security (SCA)
A dedicated scanner that keeps tabs on your open-source libraries, alerts you to malicious packages, and automatically generates clean Software Bills of Materials (SBOMs).
Checkmarx IaC Security
A proactive scanning tool that uncovers exposed API keys, active certificates, and infrastructure-as-code misconfigurations before your code ever goes live.
Checkmarx Application Security Posture Management (ASPM)
An intelligence layer that deduplicates your security findings and uses real-time runtime data to prioritize the flaws that actually pose a threat to your business.
Checkmarx Integration Architecture
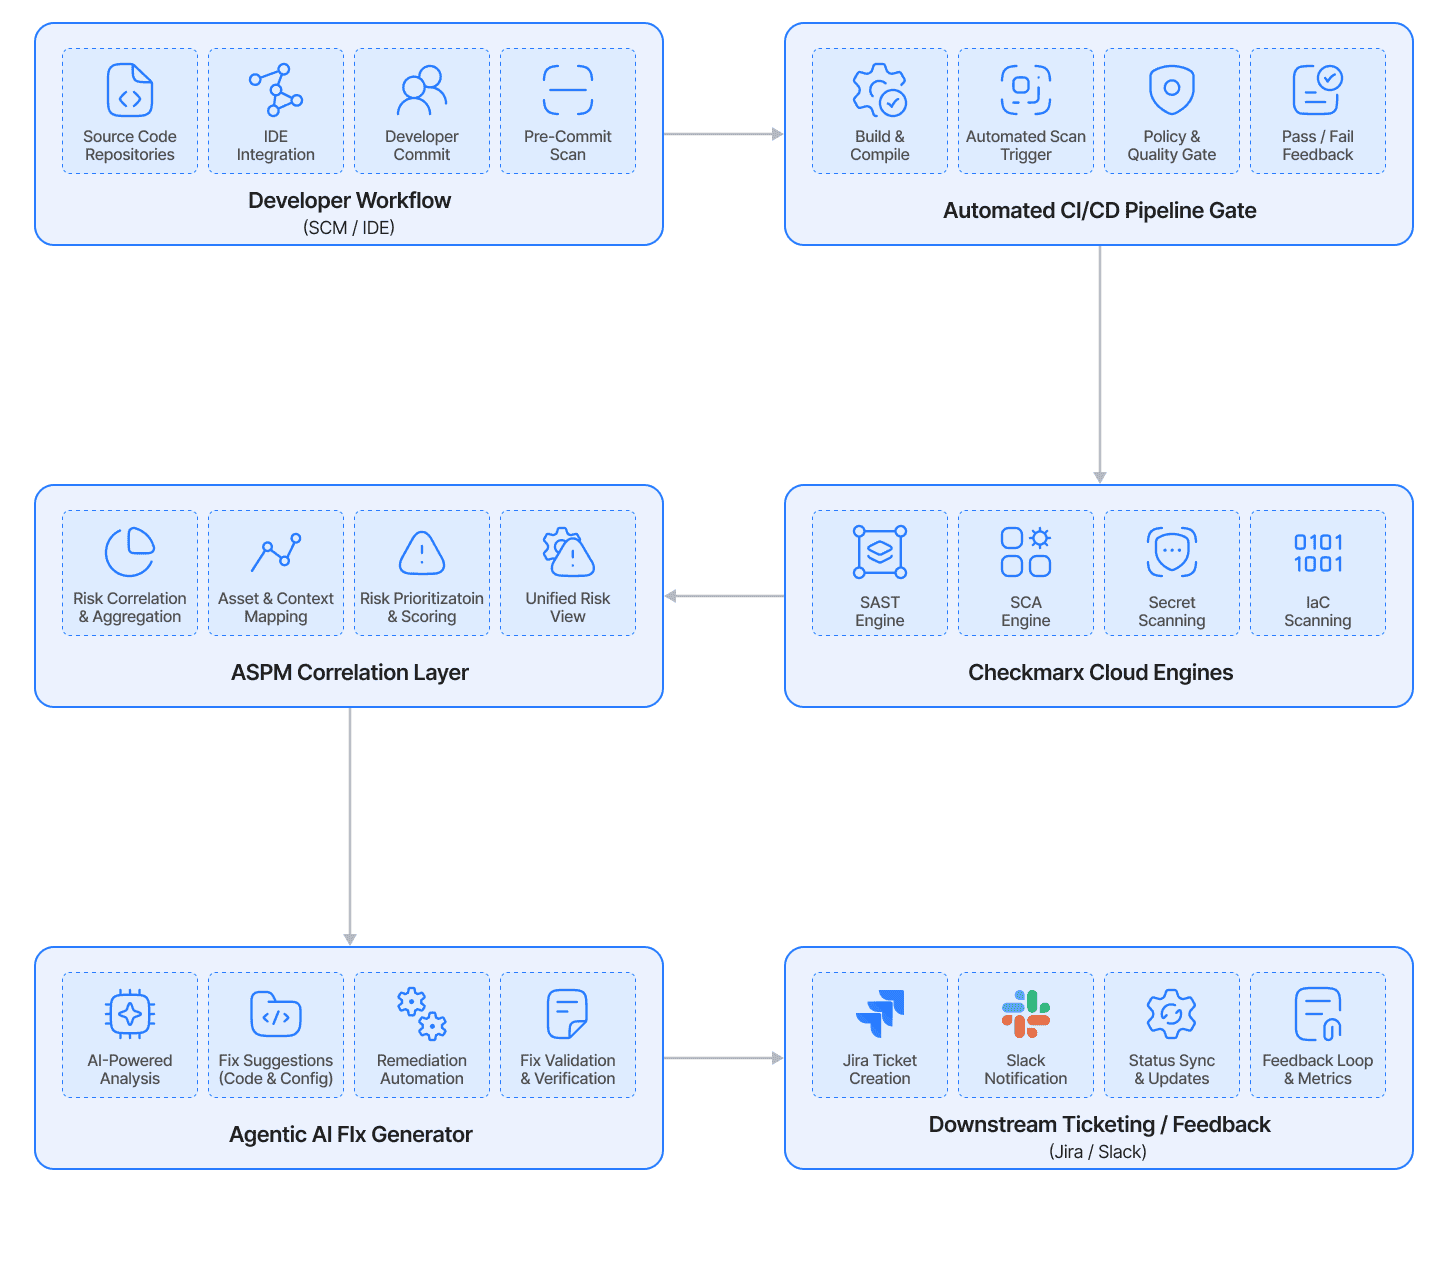
Data moves smoothly between your development environment and Checkmarx One. When an engineer commits code or runs a build pipeline, a secure webhook sends metadata about the codebase to the Checkmarx scanning engines. The platform runs its tests, filters out the noise through its ASPM layer, and pushes actionable security fixes and risk analysis directly back into the developer's native workspace.
Streamlined Logic
1. Trigger: A developer pushes code or opens a new pull request in their repository.
2. Ingest: The code management tool securely passes repository metadata to the Checkmarx cloud via webhooks.
3. Analyze: Checkmarx parallel engines quickly test the code for custom flaws, open-source risks, and leaked secrets.
4. Correlate: The ASPM layer cross-references runtime exposure data to isolate the truly critical vulnerabilities.
5. Remediate: The built-in AI assistant drafts a tailored, safe code modification to fix the identified risk.
6. Delivery: The integration posts the results directly inside the developer's pull request or creates a tracked ticket in Jira.
Checkmarx Integration Benefits
Code Repository & SCM Connections
Hooks straight into platforms like GitHub, GitLab, and Bitbucket to scan code automatically on every git push or pull request.
CI/CD Pipeline Automation
Inserts quick security checkpoints into your build workflows, including Jenkins, GitHub Actions, and Azure DevOps, to catch vulnerabilities before deployment.
IDE Developer Extensions
Plug directly into your coding environment (like VS Code or JetBrains) so you can scan your code and fix errors as you type.
Ticketing & Slack Notifications
Syncs security alerts straight to the tools your team uses daily, automatically opening, updating, or closing issues in Jira and sending alerts to Slack.
Cloud & Runtime Context
Connects with live environments like AWS or CrowdStrike Falcon to map active production containers back to their source code for better risk analysis.
Integration Use Cases
Automated Pull Request Guardrails
You can set up automated quality gates that analyze code updates in real time. If a pull request introduces a critical bug or breaks a company's compliance policy, the integration pauses the merge until the code is corrected.
Filtering Noise with ASPM
The system checks your actual runtime environment to see if a vulnerable open-source library is active and reachable by your application. This filters out irrelevant alerts and cuts down your security noise by up to 95%.
Frictionless Developer Loops
Instead of making developers jump between different platforms, security findings show up directly in their code editor or repository view. The integration provides ready-to-merge code fixes, shrinking the time it takes to fix bugs.
Similar Connectors