Transform Enterprise Security with 1Password Integrations
Overview
1Password safeguards sensitive enterprise data through an end-to-end encrypted, zero-knowledge architecture. By connecting 1Password across your infrastructure, identity, and application ecosystems, we eliminate hardcoded secrets, automate identity governance, stream security events in real-time, and streamline application provisioning, without ever exposing your unencrypted data to the cloud.
Key Products
Enterprise Password Manager (EPM)
Centralizes and encrypts passwords, sensitive notes, and payment credentials across all employee devices. It enables secure vault sharing, enforces company-wide authentication policies, and synchronizes directly with identity providers like Okta and Microsoft Entra ID.
1Password SaaS Manager
Discovers and catalogs third-party software and unapproved AI tools across the organization. It enables IT teams to identify unsanctioned "Shadow AI," track LLM token expenditure, automate license allocation, and control AI agent permissions.
Privileged Access
Grants ephemeral, "just-in-time" access permissions to engineers and automated workloads operating in critical cloud environments or databases. It enforces least-privilege access by revoking credentials as soon as a task finishes.
1Password Integration Architecture
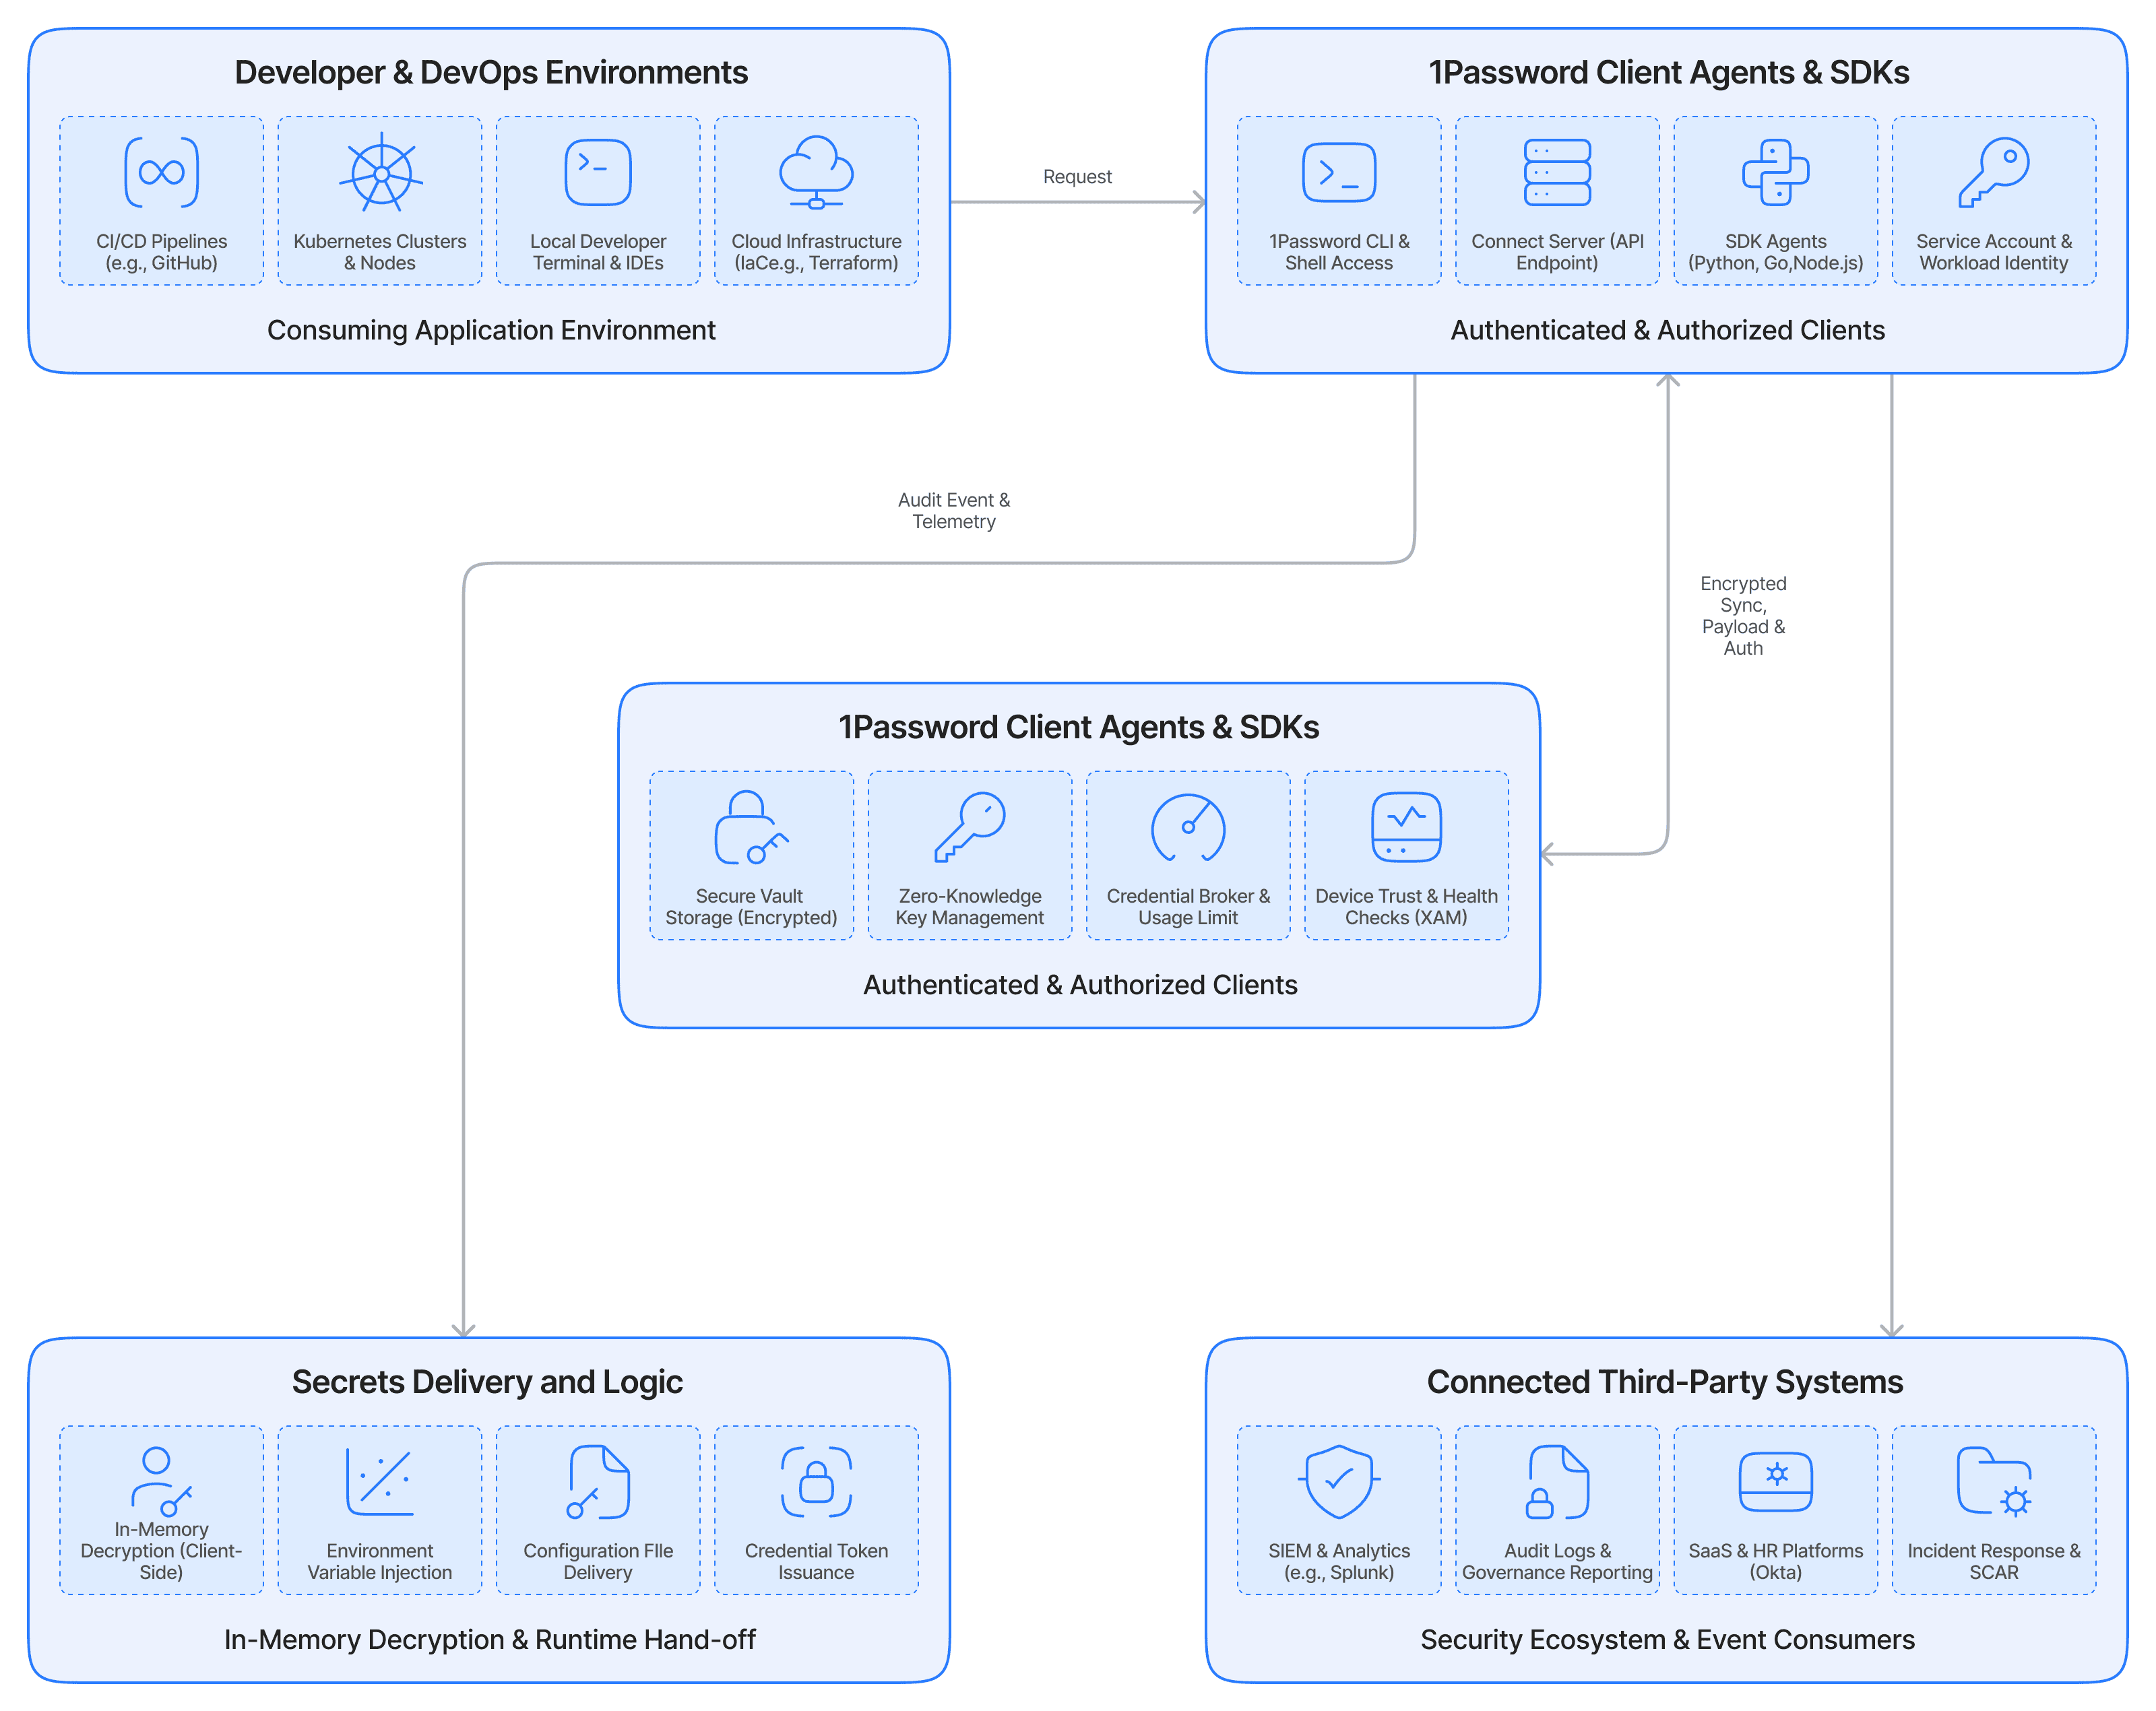
When an enterprise pipeline or developer tool requests a secret, the request routes to a local, client-side container or CLI agent (e.g., 1Password Connect or CLI) authenticated via an encrypted Service Account token. The local service fetches the encrypted secret blob from the 1Password Cloud, decrypts it locally in memory using the client-side keys, and passes the plaintext secret directly to the consuming process, ensuring the secret never persists on disk or travels unencrypted over the network.
Streamlined Logic
1. Trigger Request: A pipeline, application, or developer command requests a specific vault secret or access authorization.
2. Local Authentication: The client component (1Password CLI or Connect Server) validates the request using a scoped Service Account or biometric authorization.
3. Encrypted Payload Fetch: The authenticated client fetches the zero-knowledge encrypted vault item from the 1Password Cloud API.
4. In-Memory Decryption: The client decrypts the payload locally using private keys stored in the local enclave or key file.
5. Runtime Injection: The decrypted secret is injected directly into the target environment variable, configuration file, or API header.
6. Audit Event Logging: The transaction details are streamed to the 1Password Events API and forwarded to your security team's SIEM for audit tracking.
1Password Integration Benefits
Zero-Trust Developer Secrets Delivery
Eliminate hardcoded API tokens, database passwords, and SSH keys in source repositories. We load secrets into your local terminals, IDEs, and CI/CD runners dynamically at execution time, preventing secret leaks and simplifying credential rotation across every environment.
Automated Lifecycle & License Governance
Streamline user provisioning and deprovisioning by linking 1Password to your existing Identity Provider (IdP) and HR systems. We sync joiner/mover/leaver events, automatically assign vault permissions based on group roles, and revoke application access instantly when employees offboard.
Real-Time Security Incident Monitoring
Gain complete visibility into user access patterns, administrative actions, and vault changes across your organization.
Infrastructure-as-Code Automation
Manage secrets within cloud infrastructure templates without compromising zero-knowledge guarantees. We supply native providers for platforms like Terraform and Pulumi, so your team can deploy scalable, cloud-native infrastructure with zero hardcoded credentials.
Integration Use Cases
Dynamic CI/CD Pipeline Credential Injection
We accelerate developer velocity by linking runtime secrets injection directly to your build and deployment pipelines. When a GitHub Action or local terminal triggers a build, the integration automatically pulls short-lived database keys into memory and wipes them immediately after execution.
Automated Identity Lifecycle & Provisioning
We eliminate security delays by connecting employee status changes in your HR system or IdP directly to vault permissions. When you offboard an employee or transition a team member's role, the integration automatically revokes access and rotates shared credentials in real time.
Automated SIEM Alerting & Incident Response
We optimize threat mitigation by streaming real-time security events directly into your SOC monitoring tools. When 1Password detects anomalous vault activity or repeated login failures, the integration automatically triggers high-priority alerts and executes lockout playbooks inside Splunk or Datadog.
Similar Connectors