Unify Security and Observability with Sumo Logic
Key Products
Log Analytics & Management
Aggregates and normalizes logs from applications, cloud platforms, and on-premises infrastructure for centralized analysis. LogReduce groups similar log messages into patterns, while LogCompare highlights changes between sets of logs to help teams identify anomalies and investigate issues faster.
Cloud SIEM
Detects and correlates security activity across your environment. Cloud SIEM turns incoming security records into signals when suspicious activity is detected and groups related signals into insights, helping analysts prioritize and investigate potential threats.
Application Observability & Distributed Tracing
Provides full-stack visibility across microservices and containerized environments. Powered by native OpenTelemetry (OTel) standards, it correlates end-to-end distributed transaction traces with log data and APM metrics to pinpoint performance bottlenecks.
Cloud SOAR
Automates and orchestrates incident response through customizable playbooks and integrations. It helps security teams enrich alerts, coordinate investigations, and execute remediation actions across connected security tools.
Infrastructure Monitoring
Offers continuous monitoring and out-of-the-box dashboards for Kubernetes, Docker containers, serverless components, and major cloud providers (AWS, Azure, GCP).
Dojo AI
Multi-agent AI system designed specifically for security operations. It orchestrates automated context gathering, root-cause investigation, and threat triage to boost SOC team efficiency.
Sumo Logic Integration Architecture
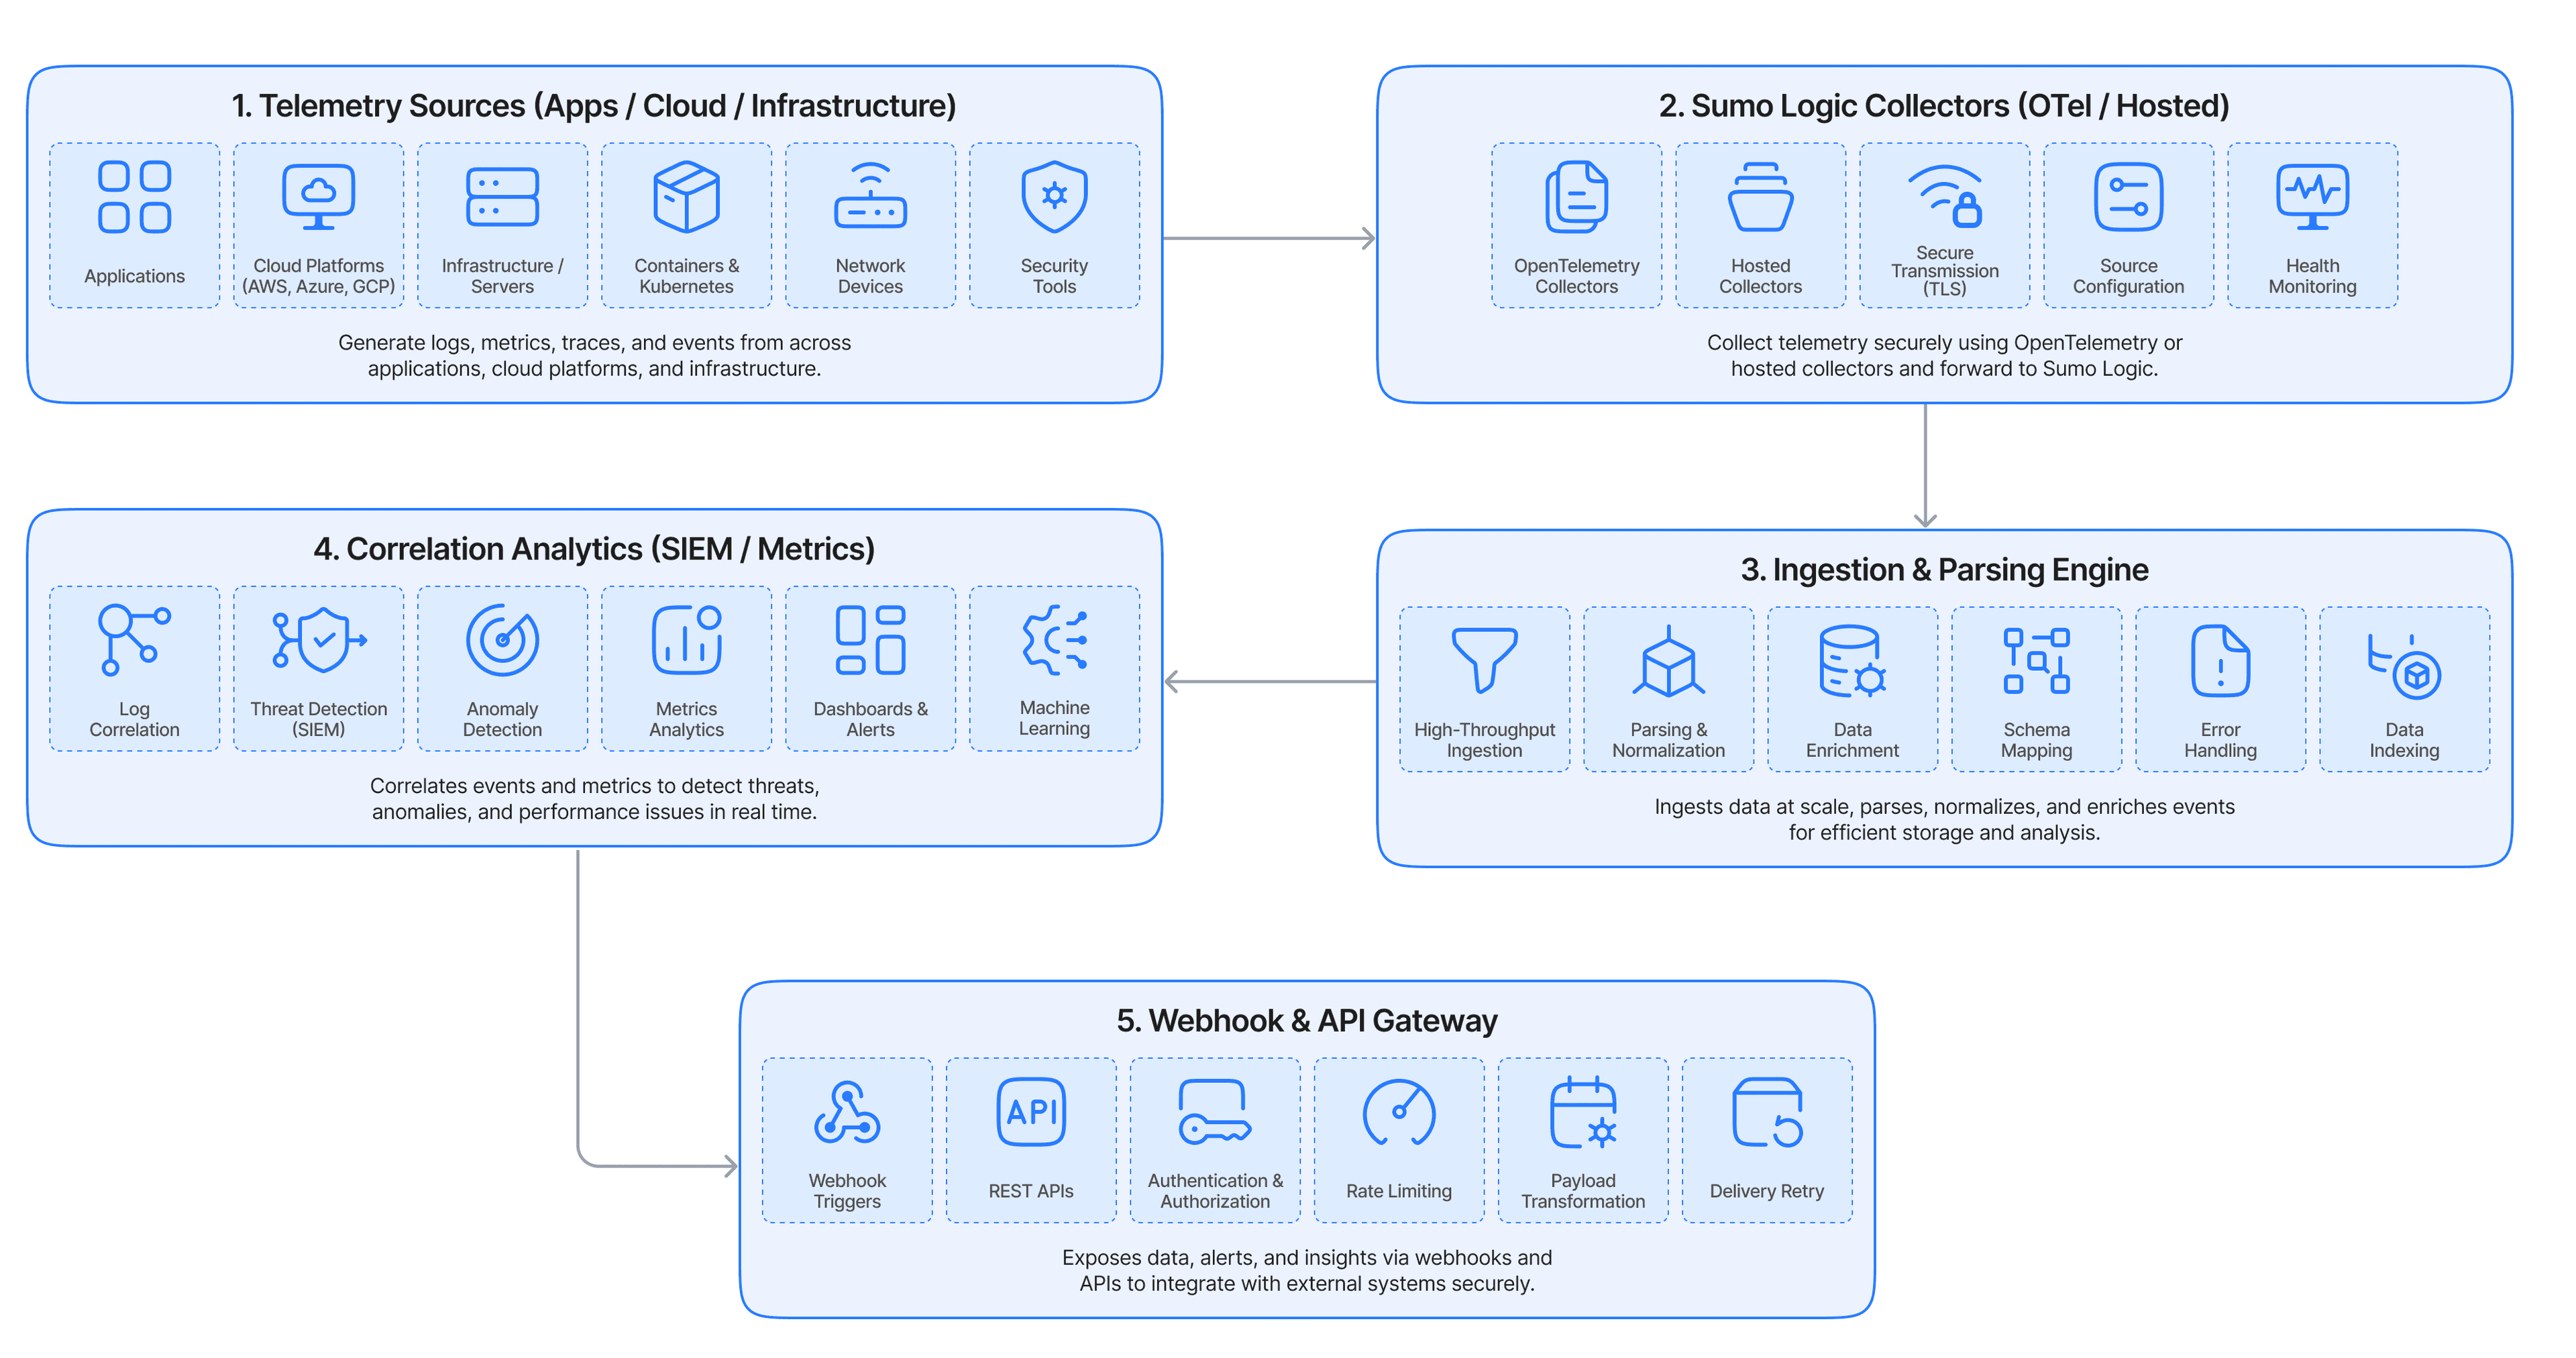
Data flows continuously from external application components and cloud infrastructure into Sumo Logic's ingestion engine for real-time parsing, indexing, and threat correlation. When an operational anomaly or security threshold is triggered, Sumo Logic dispatches enriched incident data outward to third-party communication channels, ticketing tools, or automated response playbooks.
Architecture
1. Data Ingestion: Remote hosts, cloud services, and microservices send raw logs, metrics, and traces into Sumo Logic via OpenTelemetry collectors or hosted OTLP endpoints.
2. Parsing & Normalization: Sumo Logic extracts key metadata fields and normalizes security records into standard schemas.
3. Analytics & Correlation: The analytics engine executes continuous search jobs, evaluates rules, applies UEBA behavioral detection, and correlates events against threat intelligence feeds.
4. Alert Triggering: When query parameters or threat detection rules trigger, Sumo Logic compiles an alert payload with search context and deep-link references.
5. Outbound Execution: A configured webhook posts the alert payload to downstream ITSM, messaging, or SOAR platforms to initiate automated triage or human response.
Sumo Logic Integration Benefits
Installed & OpenTelemetry Collectors
Deploy lightweight, host-based collectors directly on virtual machines, local servers, or Kubernetes pods to gather system metrics, application logs, and local event streams.
Hosted Collectors & OTLP Endpoints
Cloud-managed ingestion endpoints that receive push-based telemetry via standard HTTPS REST calls, direct CloudSyslog streams, or native OpenTelemetry Protocol (OTLP/HTTP and OTLP/gRPC).
Cloud-Native Event Streaming
Connect cloud data sources using provider-native ingestion mechanisms such as AWS Kinesis Data Firehose, Azure Event Hubs, and Google Cloud Pub/Sub.
Outbound Webhook Connections
Send real-time notifications and customized payload alerts from Sumo Logic scheduled searches directly into external endpoints like Slack, PagerDuty, Jira, or custom API gateways.
REST APIs & Developer SDKs
Enable programmatic management of Sumo Logic integrations, including querying search jobs, managing collector configurations, accessing platform data, and connecting analytics with custom internal tools.
Integration Use Cases
OpenTelemetry-Based Full-Stack Observability
We configure standardized OpenTelemetry pipelines across your application microservices. By routing traces, metrics, and logs into Sumo Logic, we enable instant cross-layer correlation during outages, cutting mean time to resolution (MTTR) without locking you into proprietary agents.
Closed-Loop Incident Remediation
We integrate Sumo Logic monitors with cloud orchestration tools and outbound webhooks. When operational error rates breach critical thresholds, our integration automatically executes server scale-out actions, restarts failed pods, or triggers network isolation playbooks.
Compliance & Long-Term Audit Archiving
We construct programmatic data pipelines utilizing Sumo Logic's extraction APIs to automatically stream indexed compliance logs into long-term cloud storage vaults (such as AWS S3 Glacier), satisfying regulatory retention mandates with zero manual overhead.
Similar Connectors