Unify Privileged Access Security with Delinea
Key Products
Delinea Secret Server
Enterprise-grade credential vaulting, automated password rotation, session recording, and just-in-time access management for privileged accounts across servers, databases, and network equipment.
Delinea Privilege Manager
Endpoint least-privilege enforcement and application control that removes local admin rights on Windows and macOS workstations while allowing authorized application elevation.
Delinea DevOps Secrets Vault
High-velocity, low-latency API secret management engineered specifically for CI/CD pipelines, container orchestration platforms (Kubernetes), and microservice micro-segmentation.
Delinea Privilege Control for Cloud Entitlements (CIEM)
Multi-cloud identity analytics and entitlement right-sizing across AWS, Azure, and GCP to detect and remediate overly permissive identities.
Delinea Identity Threat Protection (ITDR)
Real-time identity vulnerability monitoring and attack path visualization that flags compromised credentials and anomalous privileged behavior.
Delinea Fastpath Access Control
Continuous SaaS identity governance and segregation of duties (SoD) monitoring across business-critical enterprise applications.
Delinea Integration Architecture
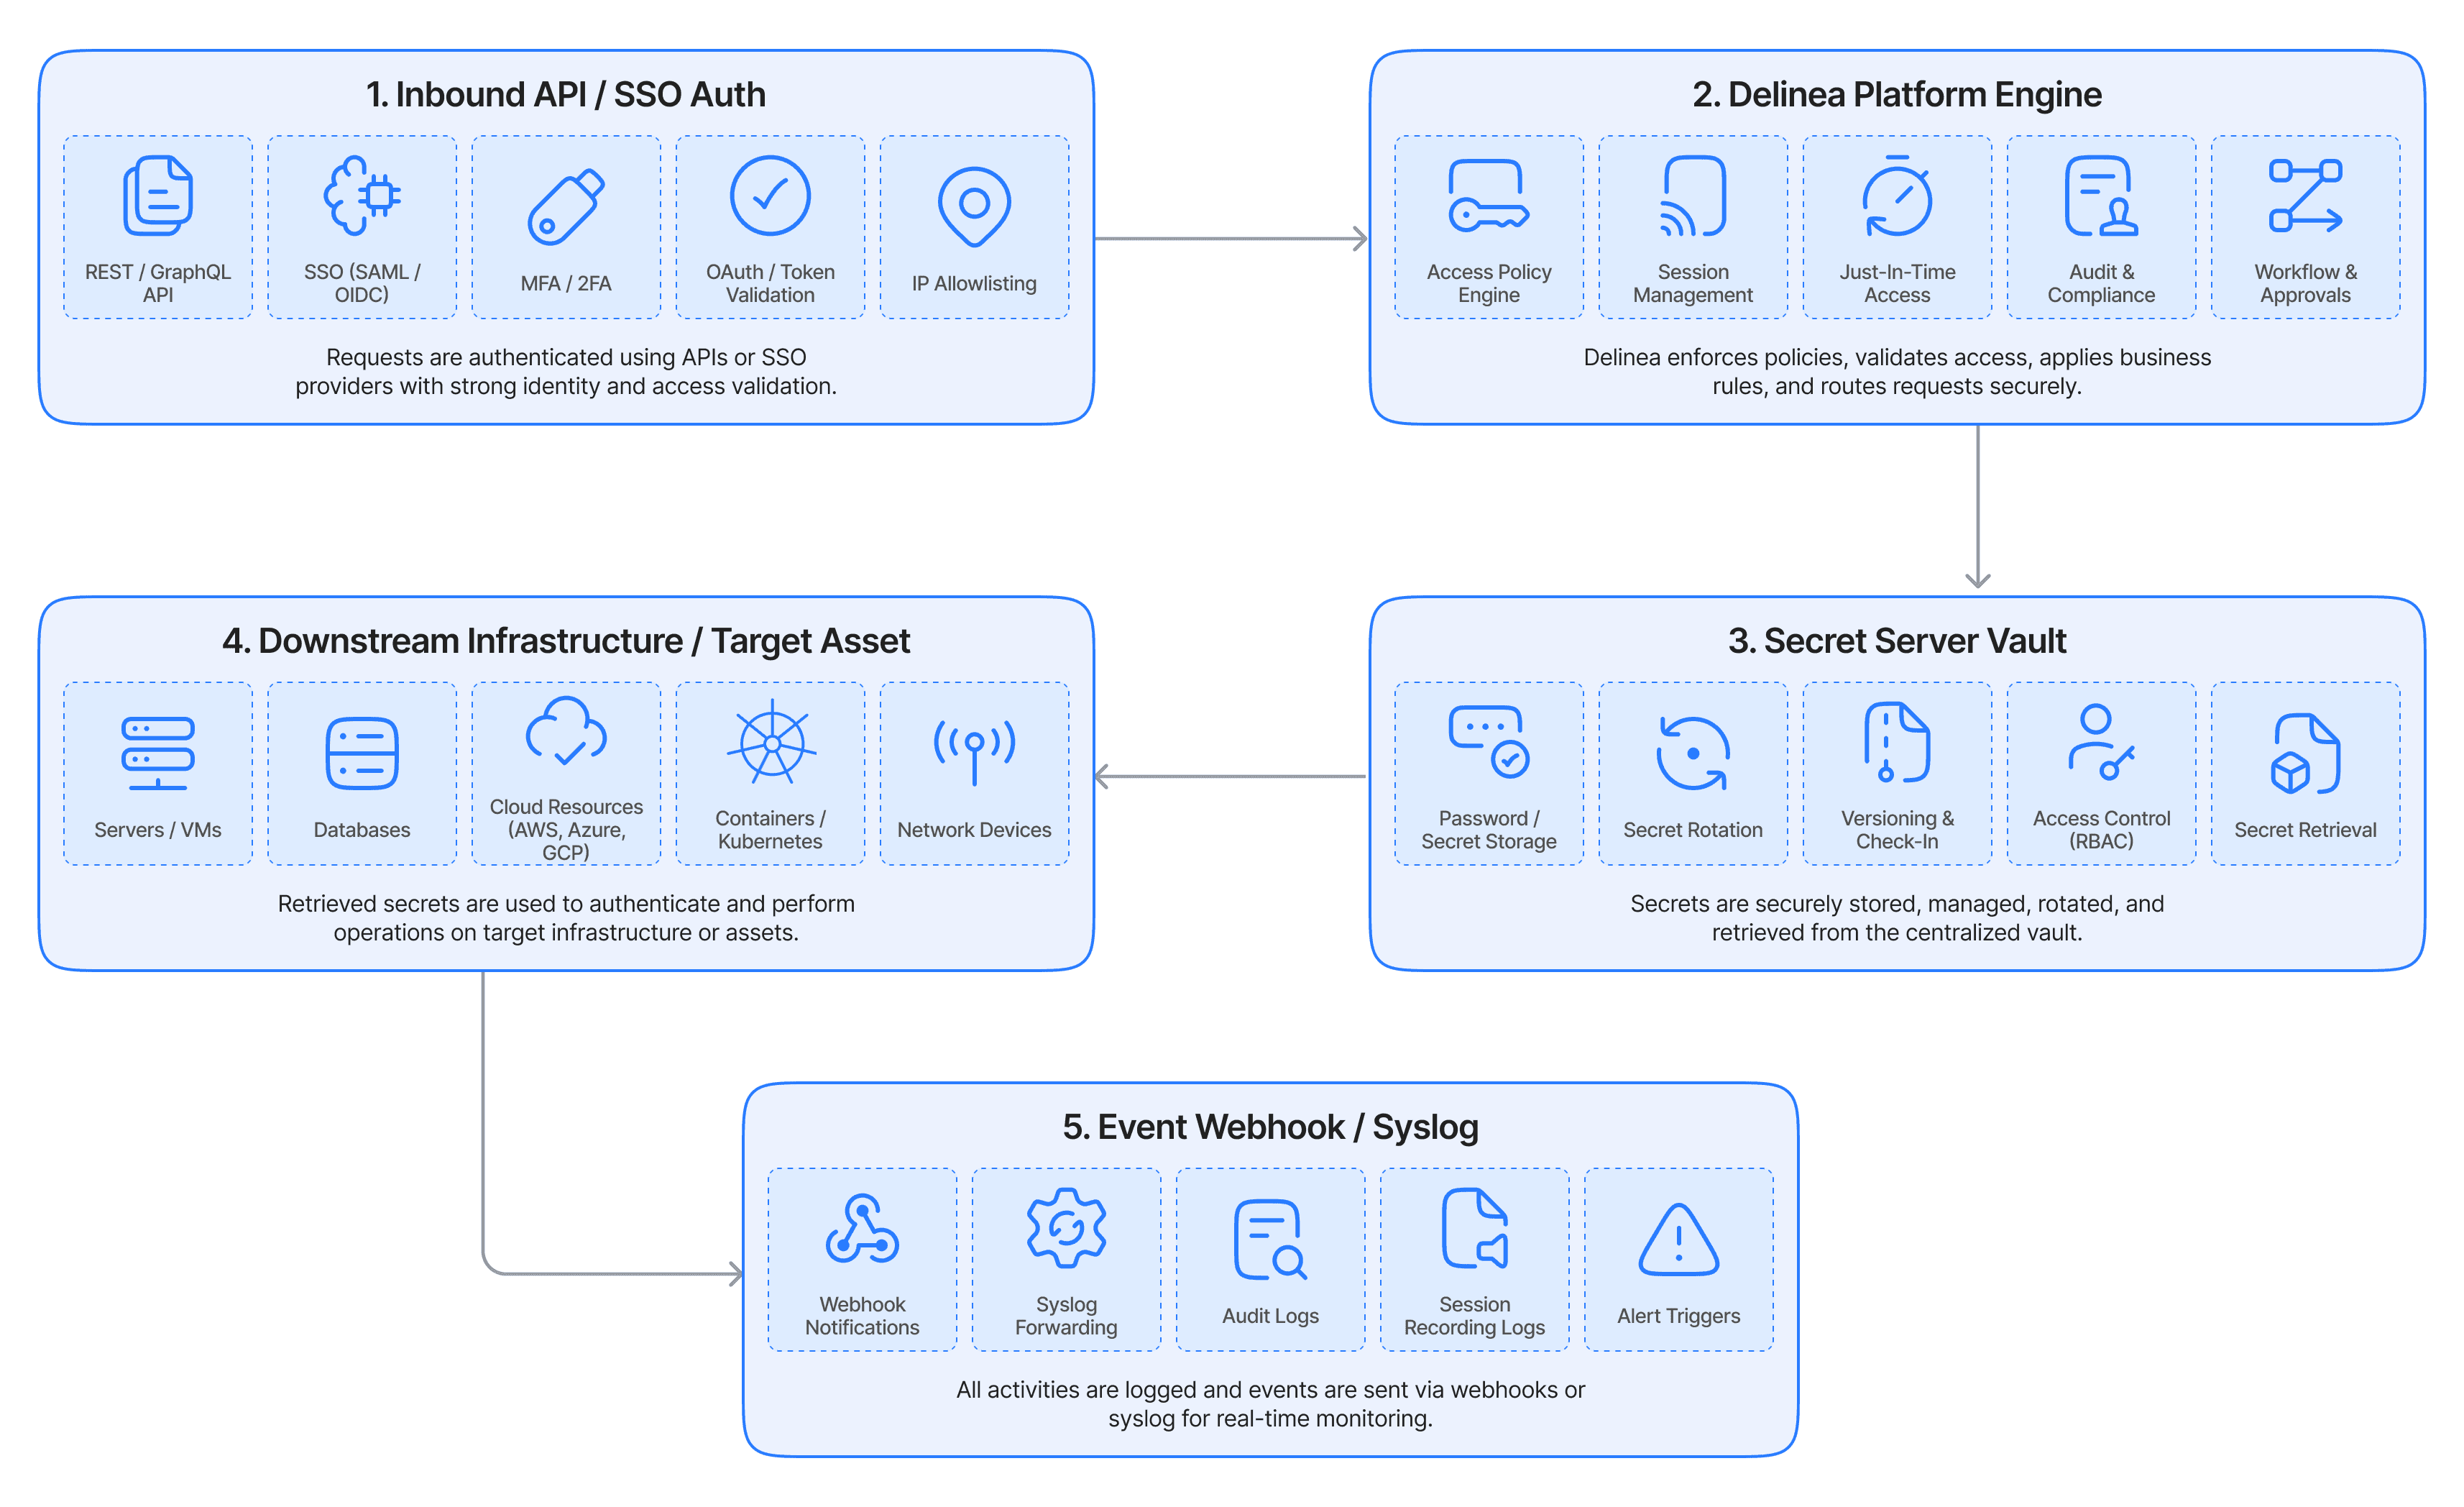
Delinea connects with external security and IT platforms to manage privileged access and share security events. Through secure APIs and integrations, it validates access requests, manages credentials through Secret Server, and forwards audit logs to SIEM/SOAR tools for continuous monitoring and automated response.
Architecture
1. Authentication & Identity Verification: The target application or user authenticates against Delinea via SAML/OIDC or API Token.
2. Entitlement & Policy Check: Delinea checks active authorization policies, ticket approval status, and risk scoring for the requester.
3. Credential Retrieval / Session Proxying: Delinea retrieves encrypted credentials from Secret Server or initiates an isolated proxied session.
4. Target Execution: The application or user connects to the downstream server, database, or API without exposing raw credentials.
5. Telemetry Stream & Event Export: Delinea streams audit logs, keystroke recordings, and security events to connected SIEM and ITDR tools.
Delinea Integration Benefits
REST API & SDK Integration
Query secrets, trigger password rotations, and request elevated privileges programmatically using Delinea’s REST APIs and language-specific SDKs built for automation pipelines.
Native Marketplace Connectors
Plug pre-packaged Delinea Marketplace modules directly into enterprise ITSM, SIEM, and IAM platforms to stream logs and automate ticket-driven access workflows out-of-the-box.
Webhooks & Event Ingestion
Push real-time privilege elevation requests, secret checkouts, and session monitoring events directly to external Webhook endpoints or SOAR automated playbooks.
SIEM & Syslog Log Exporters
Stream formatted audit trails, session logs, and access events using standard Syslog (CEF/LEEF) or dedicated API telemetry exporters for threat analytics.
Custom Scripting Hooks & Extenders
Execute PowerShell, Python, or Shell scripts natively within Delinea Secret Server to update custom downstream target systems during credential lifecycle events.
Integration Use Cases
Centralized Audit & SIEM Telemetry Streaming
We ingest audit logs, credential checkout actions, and video session recordings from Delinea into SIEM solutions like Splunk, Microsoft Sentinel, and Datadog. This gives SOC analysts unified visibility into privileged user behavior alongside network threat intelligence.
High-Velocity CI/CD Pipeline Secret Injection
We connect Delinea DevOps Secrets Vault directly to GitHub Actions, GitLab CI, Jenkins, and Terraform. Developers dynamically inject ephemeral credentials directly into build jobs without storing static secrets inside source repositories.
Automated Incident Response & Session Termination
We wire Delinea event webhooks into SOAR platforms like Palo Alto XSOAR and Swimlane. If an endpoint security system detects malicious behavior, the integration automatically triggers Delinea to terminate active privileged sessions and lock compromised accounts instantly.
Similar Connectors