Secure IT, OT, and IoT Environments with Nozomi Networks
Overview
Nozomi Networks provides comprehensive visibility, threat detection, and AI-driven insights across operational technology (OT), IoT, and IT environments. Built to protect critical infrastructure, it helps organizations discover assets, monitor industrial networks, and detect cyber threats in real time. Integrating with Nozomi Networks extends operational visibility across your security ecosystem, enabling faster threat detection, incident response, and protection of critical operations.
Key Products
Nozomi Vantage
A cloud-hosted SaaS platform that provides scalable cybersecurity management and immediate visibility across globally distributed OT, IoT, and IT deployments.
Nozomi Guardian
A physical or virtual appliance that deploys at the local network level to provide continuous passive monitoring, deep packet inspection, and real-time anomaly detection.
Nozomi Central Management Console (CMC)
An on-premises or cloud deployment that aggregates data from multiple Guardian sensors, allowing centralized operations and data management for massive physical deployments.
Nozomi Arc
An endpoint intelligence sensor that delivers continuous endpoint visibility, user activity logging, and resource monitoring without disrupting mission-critical industrial assets.
Nozomi Threat Intelligence
A continuously updated feed that delivers curated, real-time threat indicators, vulnerability profiles, and signatures directly to your security appliances.
Nozomi Asset Intelligence
A dynamic profile database that uses machine learning to enrich discovered assets, helping you accurately identify vendor details, firmware versions, and Purdue Model placements.
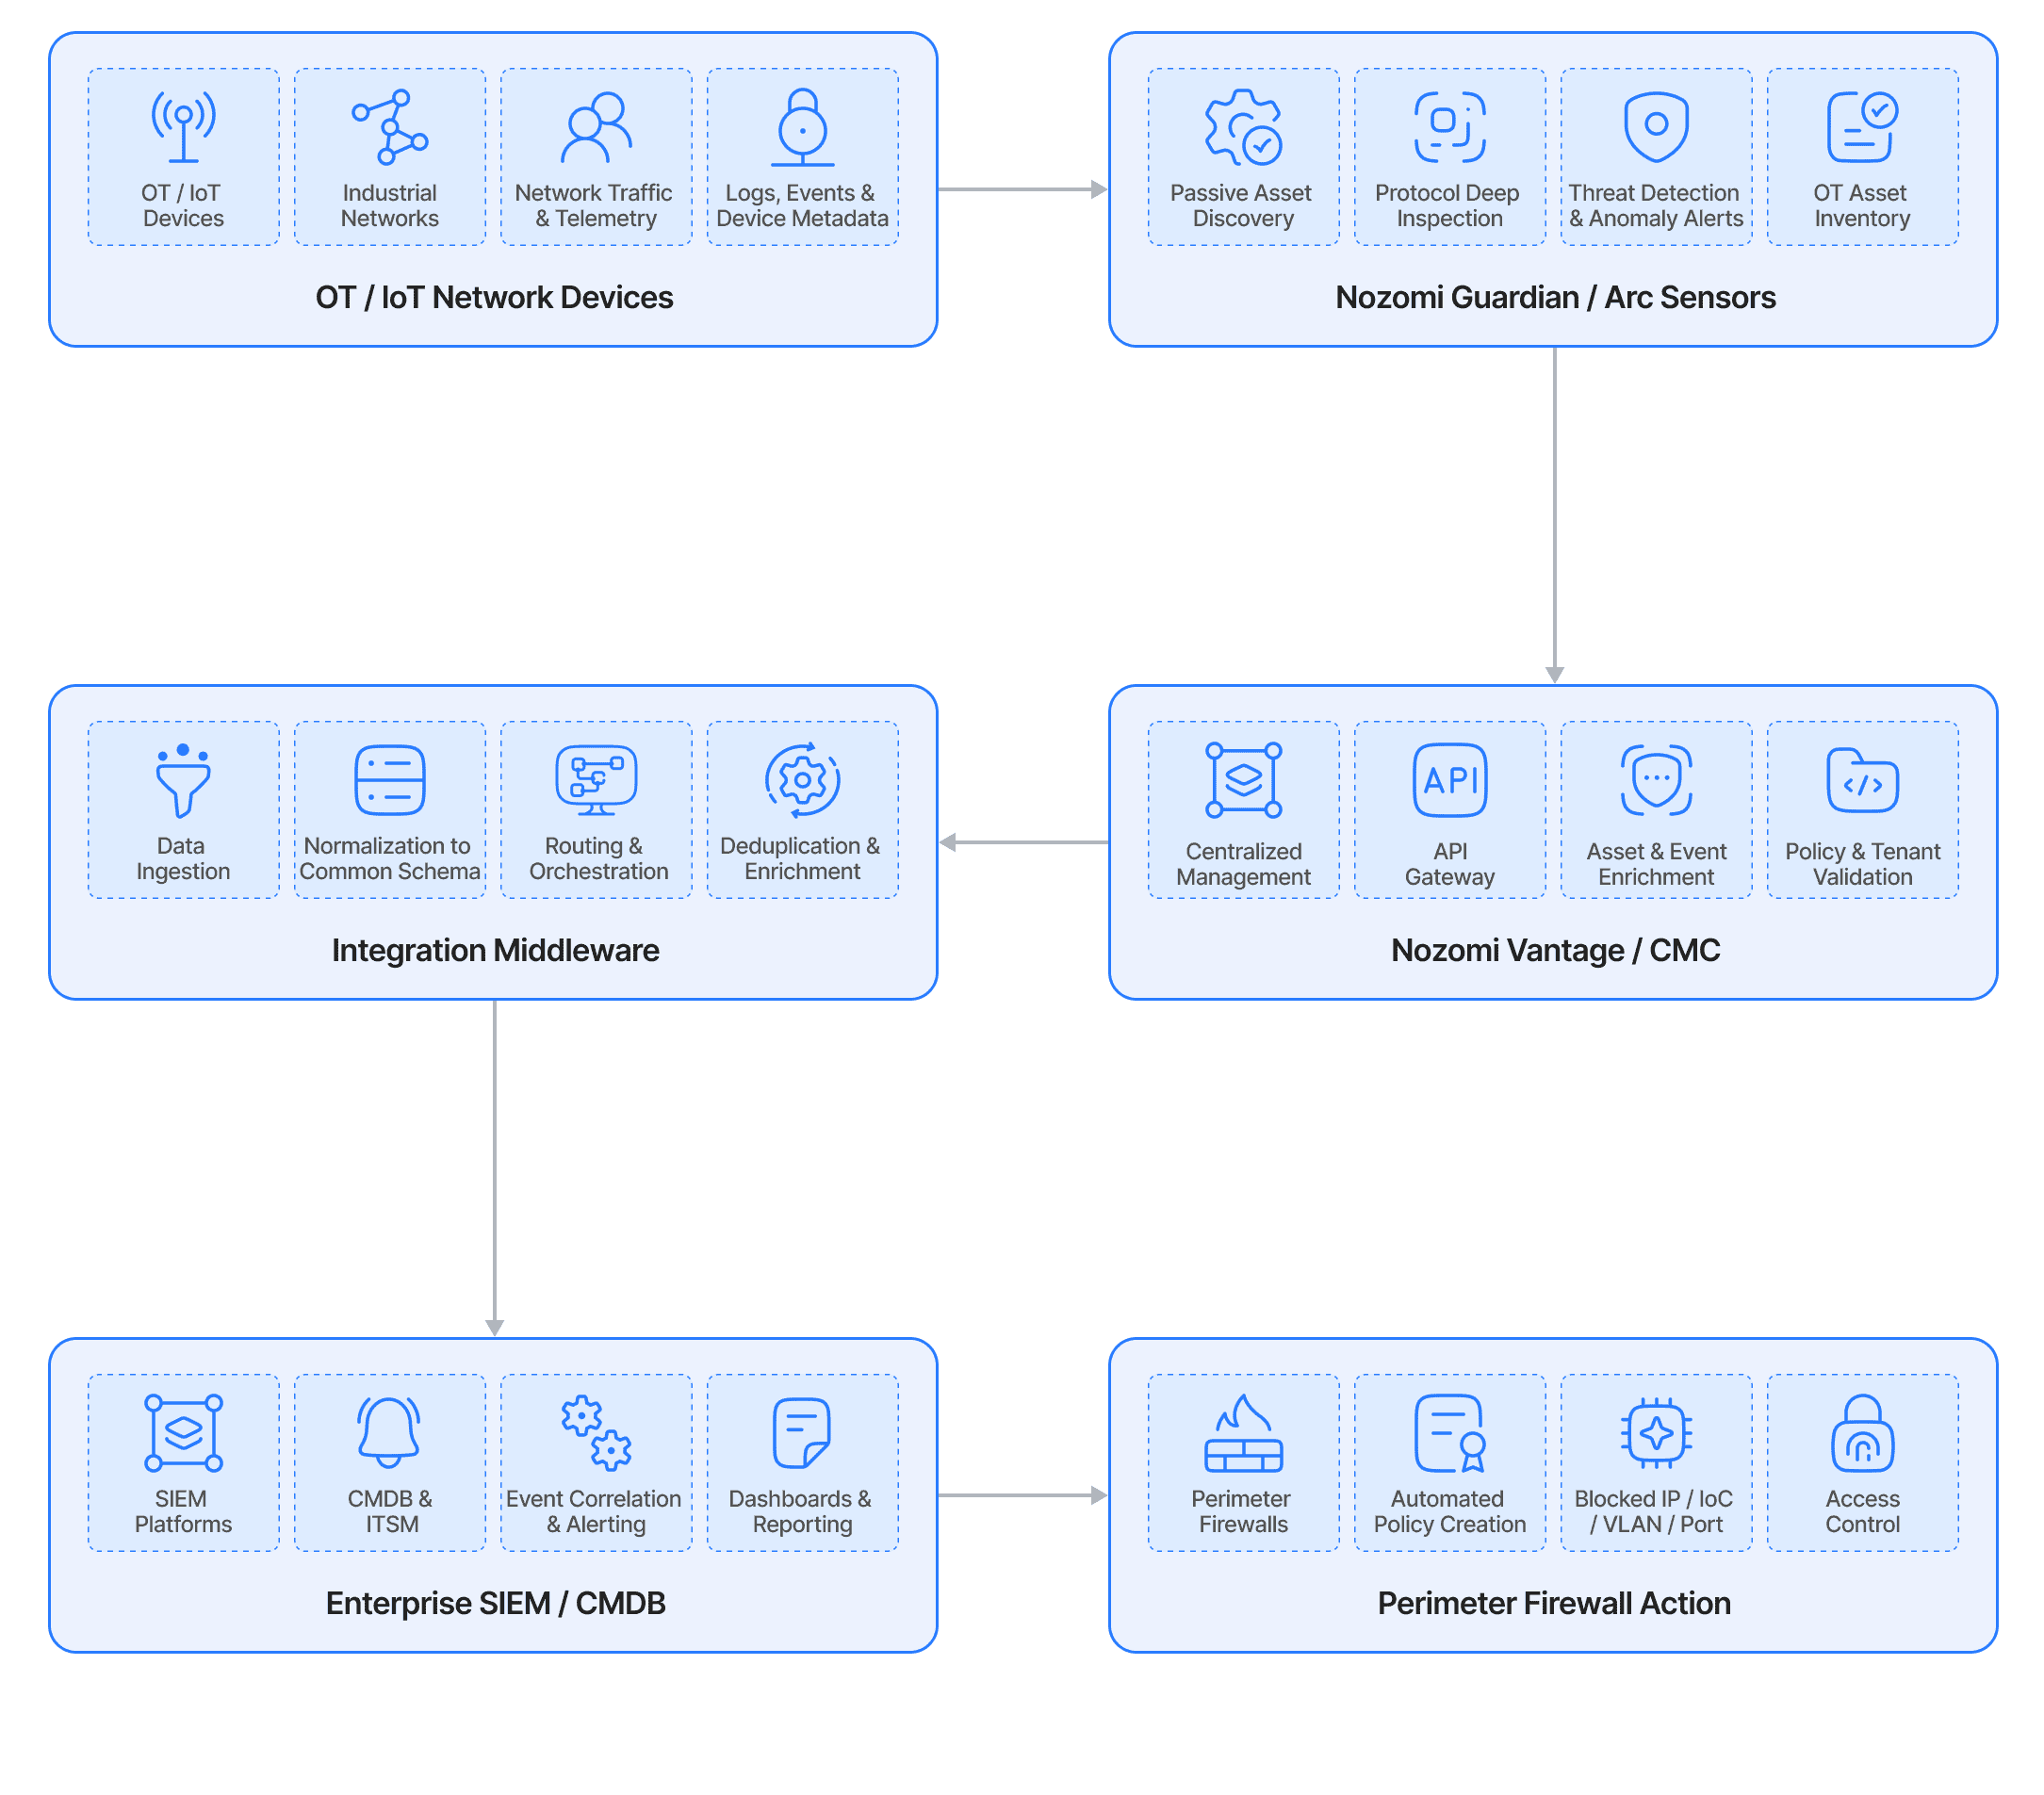
Nozomi Networks Integration Architecture
The integration enables continuous, bidirectional communications between the industrial perimeter and enterprise operations. Nozomi Networks sensors extract deep industrial data passively from the network or endpoints, normalize it, and expose it via a robust API framework. Third-party SIEMs, firewalls, and asset directories consume or pull this normalized telemetry to orchestrate security actions or centralize infrastructure views.
Streamlined Logic
1. Passive Ingestion: The integrated application requests incremental vulnerability or asset findings via Tenable's paginated REST endpoints.
2. AI Enrichment: The integration processes the asset metadata fields to compute unique identities using composite keys (such as hostUniqueness attributes, MAC addresses, or cloud IDs).
3. CAPI Exposure & Querying: The pipeline evaluates the Asset Criticality Score (ACS) and severe vulnerability status against current threat indicators.
4. SIEM / CMDB Sync: Normalized alerts and findings route cleanly to downstream IT ticketing, CMDB repositories, or active threat response engines for immediate remediation.
5. Automated Enforcement: If an alert crosses a critical threshold, the integrated middleware pushes an immediate blocking request back down to perimeter firewalls.
Nozomi Networks Integration Benefits
Asset Ingest and Synchronization
Pull comprehensive OT/IoT asset lists out of Nozomi Networks platforms and automatically sync them into enterprise asset lifecycle management tools or CMDBs like ServiceNow and Microsoft MECM.
Alert & Event Ingest
Push real-time network anomalies, malicious activity detections, and system logs to SIEM/XDR platforms such as IBM QRadar, Splunk, Elastic, and Datadog.
Network Security & Segmentation Enforcements
Dynamically translate detected threat insights into immediate policy actions by sending node-blocking or session-termination triggers to firewalls and network access controls (NAC) like Fortinet FortiGate and Check Point IoT.
Vulnerability Enrichment
Feed operational hotfixes and CVE profile correlations from Nozomi Networks directly into enterprise vulnerability scanning tools to fast-track critical infrastructure risk prioritization.
Integration Use Cases
Automated Response & Remediation
Connect Nozomi Networks’ high-fidelity alerts to enterprise firewalls and NACs. We turn passive network monitoring into active perimeter defense, containing threats before they cause industrial downtime.
Enriched Asset Analytics
Sync machine-learning-driven asset intelligence directly with your CMDBs. We populate complete vendor, firmware, and Purdue model profiles without running risky active scans on sensitive OT equipment.
Cross-Domain SIEM Monitoring
Streamline your SOC under a single pane of glass. We build data streams that feed normalized OT alerts into your IT dashboards, allowing analysts to correlate malicious patterns across the entire infrastructure.
Similar Connectors