Connect Jamf to Your Enterprise Security Stack
Overview
Jamf is the clear industry standard for managing and securing Apple hardware at scale. By designing custom integrations with Jamf’s platform, we bridge the gap between native Apple device telemetry and the rest of your operations stack. Connecting Jamf with external platforms ensures real-time security updates, automated IT service management (ITSM) ticketing, and tight identity governance across your entire organization.
Key Products
Jamf Pro
The core mobile device management (MDM) platform for large-scale enterprise environments. We leverage its inventory tracking, automated app lifecycles, and Smart Groups to trigger programmatic actions across your network.
Jamf Protect
A purpose-built endpoint security and mobile threat defence tool for Apple hardware. We connect to its telemetry engines to ingest rich security logs, flag macOS malware, and execute isolation commands.
Jamf Connect
A zero-trust network access (ZTNA) and identity manager that syncs local Mac passwords with cloud identity providers. We utilize its authentication gates to verify device health before granting access to critical tools.
Jamf Integration Architecture
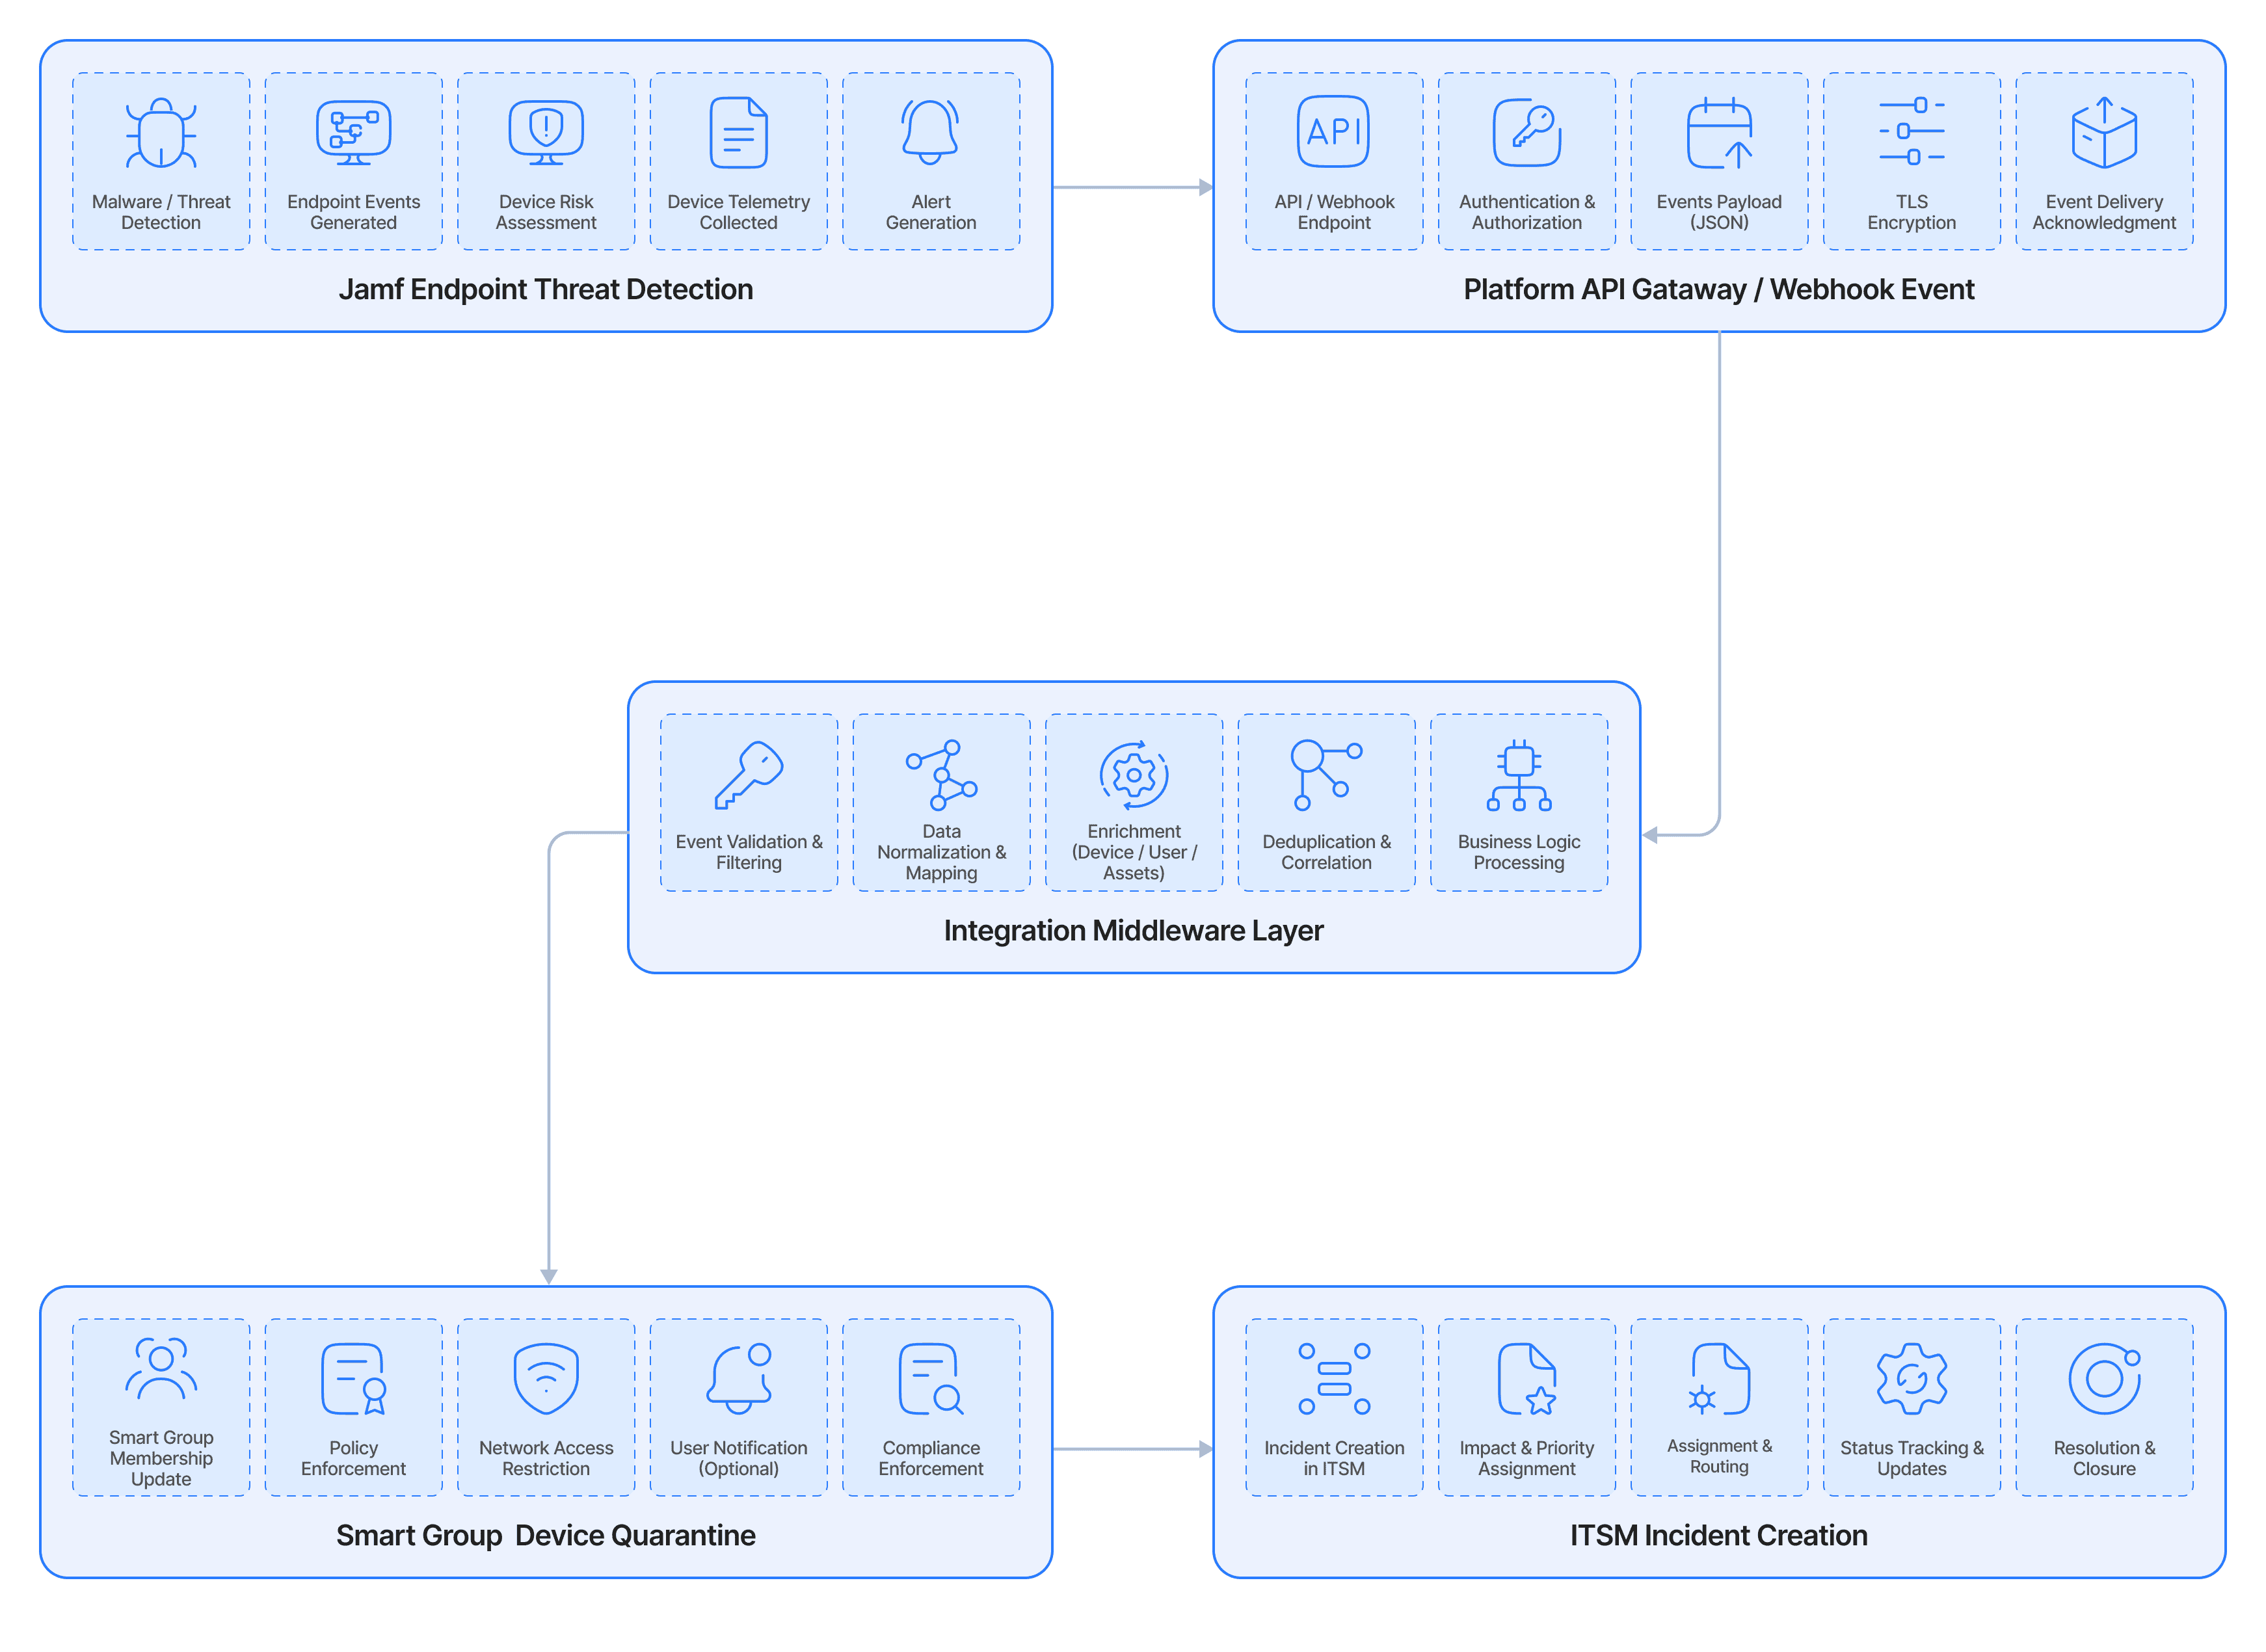
The integration constantly watches Jamf Pro inventory changes and Jamf Protect threat telemetry. When a security event arises, Jamf broadcasts a webhook alert or shared signal to our integration middleware. The middleware parses the payload, maps the user's identity, and pushes containment instructions back to Jamf while opening an escalated ticket in the enterprise ITSM platform.
Streamlined Logic
1. Ingest & Listen: The integration consumes real-time telemetry from Jamf via the API Gateway and webhooks.
2. Analyze Compliance: The system detects that a device has violated a compliance rule (e.g., disabled firewall or detected malware).
3. Enrich Context: The middleware extracts details such as serial numbers, users, and OS versions, then retrieves user groups from the identity provider.
4. Orchestrate Action: The middleware signals Jamf Pro to move the device into a quarantined Smart Group, triggering native Apple configuration overrides.
5. Log & Sync: The pipeline updates the IT asset registry and resolves or creates an alert ticket inside the operations centre.
Jamf Integration Benefits
Platform API Gateway
We build secure, centralized integrations through a single OAuth 2.0 gateway. This modern interface gives us granular, tenant-scoped control over compliance baselines and cross-product APIs.
Real-Time Webhooks
We construct event-driven pipelines by subscribing to Jamf system webhooks. When a device status changes, like falling out of a compliant Smart Group, Jamf instantly alerts external middleware to fix it.
Shared Signals Framework (SSF)
We design highly synchronized architectures that broadcast continuous risk telemetry. Implementing SSF allows a device's threat level to adjust app session permissions across your active security tools dynamically.
Managed App Configurations
We develop seamless application-level templates using standard AppConfig schemas. This lets us pre-provision enterprise applications with custom settings and backend paths before the device ever reaches the user.
Integration Use Cases
Automated Device Compliance Remediation
We eliminate manual IT monitoring by turning static inventory updates into actionable defence operations. By pairing Jamf's dynamic Smart Groups with external orchestration tools, the moment an endpoint falls below your security baseline, the system instantly revokes network privileges and pushes corrective configuration profiles.
Enterprise Threat Telemetry Ingestion
We unify isolated Apple security logs into your centralized operations data lake. Our integrations tap into Jamf's deep endpoint telemetry, enabling security operations centres to correlate macOS-specific system threats with broader network logs for faster threat response and thorough forensics.
Continuous Identity Verification and Zero-Trust Access
We safeguard corporate applications by directly linking active device compliance states to user identity checks. If an end-user's Mac develops a vulnerability gap, our integration informs the central identity engine to automatically invalidate active cloud sessions until the device passes inspection.
Similar Connectors