Secure Every Identity and Automate Zero Trust with Native Idira (formerly CyberArk) Integrations
Overview
Idira (formerly CyberArk) is a leading identity security platform that helps organizations secure privileged accounts, human identities, and machine identities across hybrid and cloud environments. Built for modern enterprises, it provides privileged access management, secrets management, identity governance, and session monitoring to reduce identity-based risks. Integrating with Idira (formerly CyberArk) extends secure identity controls across your security ecosystem, enabling stronger access protection, automated workflows, and improved operational resilience.
Key Products
Idira Privileged Access Manager (PAM)
This core module secures, rotates, and monitors privileged credentials across on-premises, hybrid, and cloud environments to neutralize the risk of credential theft.
Idira Secrets Hub
A cloud-native capability that bridges developer workflows with security policies by centrally managing secrets and synchronizing them into native cloud vaults like AWS Secrets Manager or Azure Key Vault without changing developer behaviour.
Idira Identity & Access Management
Provides single sign-on (SSO), multi-factor authentication (MFA), and automated identity lifecycle management to ensure the right users have the right access at the right time.
Idira Privileged Session Manager (PSM)
Isolates, records, and audits privileged sessions in real time, preventing malware on user endpoints from reaching critical target systems.
Idira Central Policy Manager (CPM)
Automatically rotates passwords and manages credentials across remote systems according to organizational policy without requiring manual human intervention.
Idira Privileged Threat Analytics (PTA)
Continuously monitors privileged account activity to flag anomalies, discover unmanaged assets, and trigger automatic responses to in-progress attacks.
Idira (formerly CyberArk) Integration Architecture
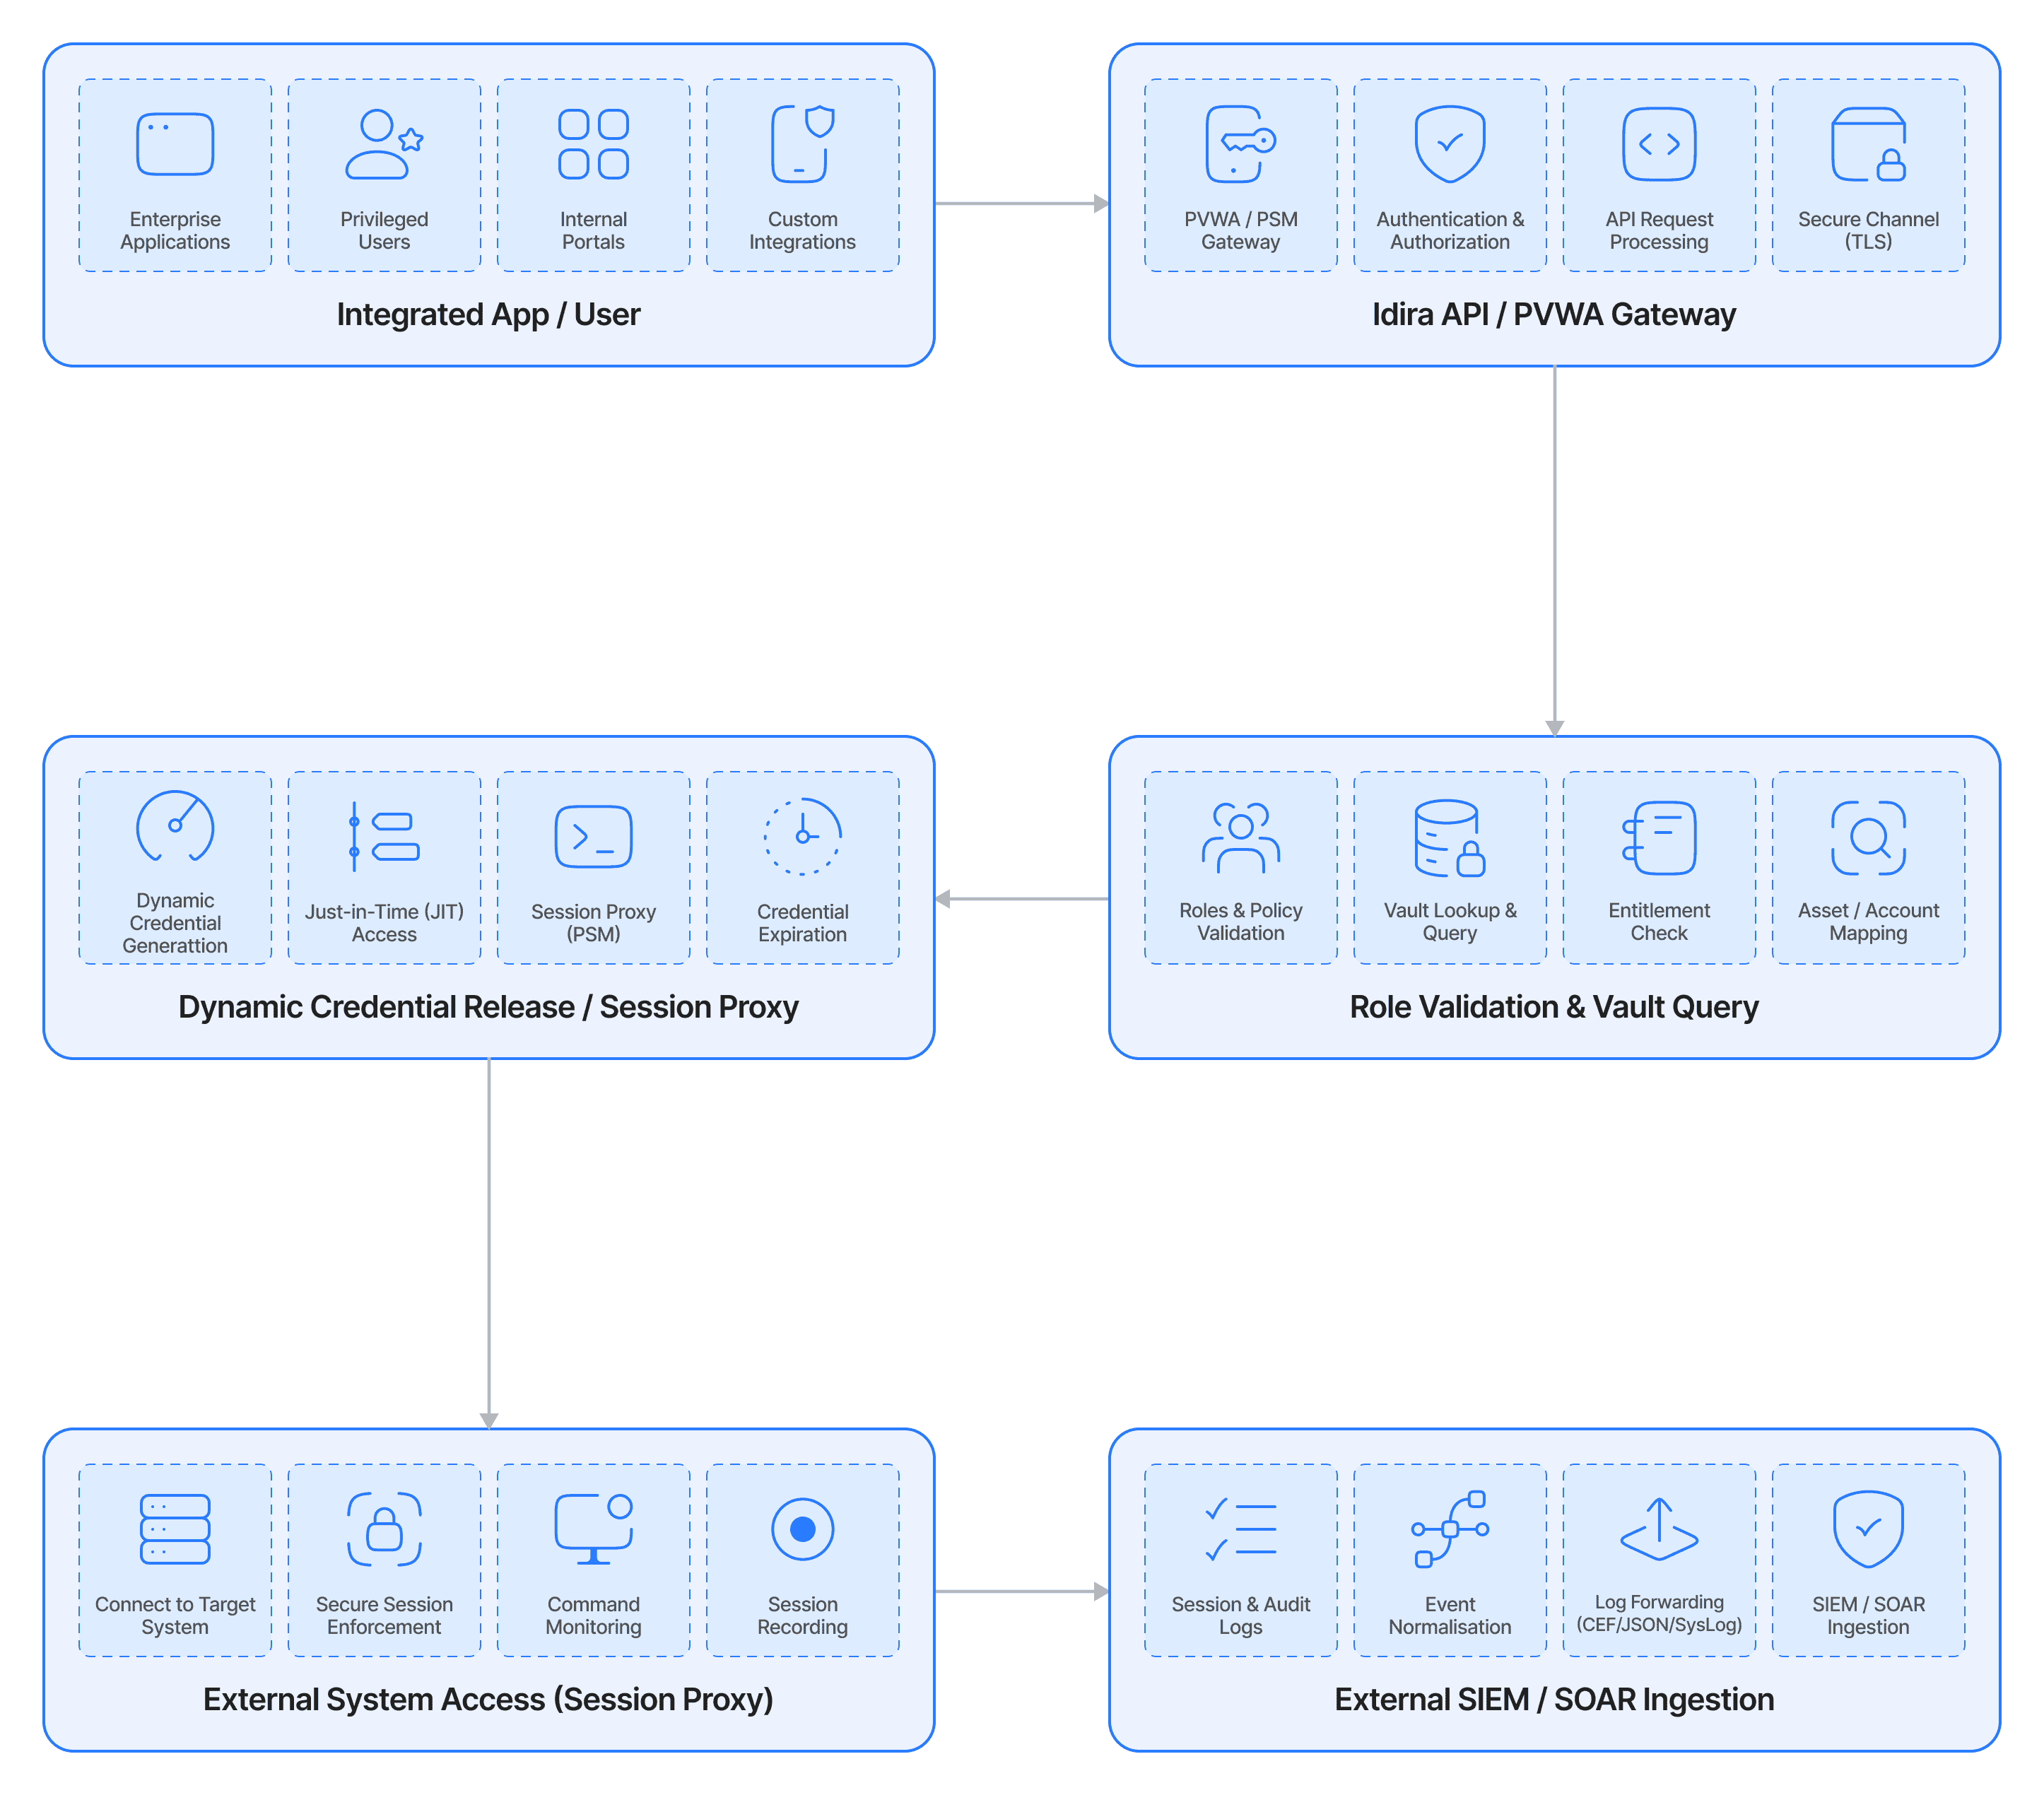
Data flows bidirectionally between external systems and the Idira platform via secure protocols. Third-party applications or users request credential access or session handling through a web interface or API gateway. Idira's Storage Engine processes this request within the isolated Digital Vault, verifies permissions against the organization's enterprise directory, and returns encrypted tokens or securely proxies the session while sending real-time log data downstream to your analytics tools.
Streamlined Logic
1. Authentication Request: An integrated application, automation tool, or privileged user initiates an authentication request through the Idira REST API or the Privileged Vault Web Access (PVWA) portal.
2. Identity Verification & Policy Evaluation: Idira validates the request against the Digital Vault or Active Directory, authenticates the identity, and enforces role-based access and security policies.
3. Credential & Session Management: The Central Policy Manager (CPM) retrieves or rotates privileged credentials, while the Privileged Session Manager (PSM) establishes a secure, isolated session to the target system.
4. Audit & Activity Logging: Idira captures session recordings, audit trails, keystroke logs, and privileged activity metadata to maintain complete operational visibility.
5. Security Monitoring & Response: Audit logs and session events are forwarded to external SIEM or SOAR platforms for threat detection, compliance reporting, incident investigation, and automated response workflows.
Idira (formerly CyberArk) Integration Benefits
Credential Rotation and Vaulting
We connect your infrastructure, databases, and network devices to Idira’s Central Policy Manager (CPM) to enforce automatic password rotation schedules and eliminate hard-coded passwords.
Secure Secrets for Machine Identities
We hook your CI/CD pipelines, containerized environments (like Kubernetes and Red Hat OpenShift), and RPA tools directly into Idira Conjur or Secrets Hub to pull dynamic secrets at runtime.
SIEM & Analytics Data Ingest
We route Idira audit trails, session recordings, and Privileged Threat Analytics (PTA) event logs directly into your SIEM or analytics platforms (such as Splunk or Falcon LogScale) to fuel real-time anomaly detection.
SOAR Actions & Incident Playbooks
We map automated workflows into SOAR platforms to instantly isolate high-risk privileged sessions or rotate compromised credentials when your security centre triggers a high-severity alert.
Ticketing & Access Request Validation
We integrate Idira’s Private Web Vault Application (PVWA) with your ITSM platforms (like ServiceNow or Jira) to validate ticket numbers and approve just-in-time access requests automatically.
Integration Use Cases
Seamless Just-in-Time Access Automation
We eliminate standing privileges by creating integrations that grant temporary, time-bound access roles based on external triggers like an active incident ticket or a scheduled maintenance window.
Zero-Friction Developer Workflows
We optimize your developer pipelines by synchronizing secrets from Idira Secrets Hub straight into your native cloud service providers, allowing engineers to continue using their preferred cloud-native toolsets without introducing compliance risks.
Proactive Real-Time Threat Remediation
We design closed-loop security integrations that allow your SOC tools to talk directly back to Idira, instantly terminating a live privileged session or executing an emergency credential rotation the second an anomaly is detected.
Similar Connectors