Automate Your Defence with Frictionless Recorded Future Integrations
Overview
Recorded Future delivers AI-powered threat intelligence by continuously analyzing data from the open, deep, and dark web to identify emerging threats, vulnerabilities, and adversary activity. Built for modern security teams, it provides actionable intelligence that helps organizations prioritize risks and respond faster. Integrating with Recorded Future extends threat intelligence across your security ecosystem, enabling faster detection, enriched investigations, and more informed security decisions.
Key Products
Recorded Future Threat Intelligence
Unmasks threat actors, charts their tactics, techniques, and procedures (TTPs) across the MITRE ATT&CK framework, and surfaces macro risk trends affecting your specific sector.
Recorded Future SecOps Intelligence Module
Accelerates daily alert validation and event triaging inside operational dashboards, allowing responders to sort through network noise and address critical alerts up to ten times faster.
Recorded Future Vulnerability Intelligence
Tracks real-world exploitation in real time and delivers dynamic risk scores for CVEs long before they hit traditional NVD timelines, giving you absolute patching clarity.
Recorded Future Integration Architecture
We connect the Recorded Future Intelligence Cloud to your local or cloud security tools via high-speed API endpoints. Data moves continuously behind the scenes, allowing your systems to pull down bulk enrichment, ingest targeted alerts, and sync asset watch lists with zero friction.
Streamlined Logic
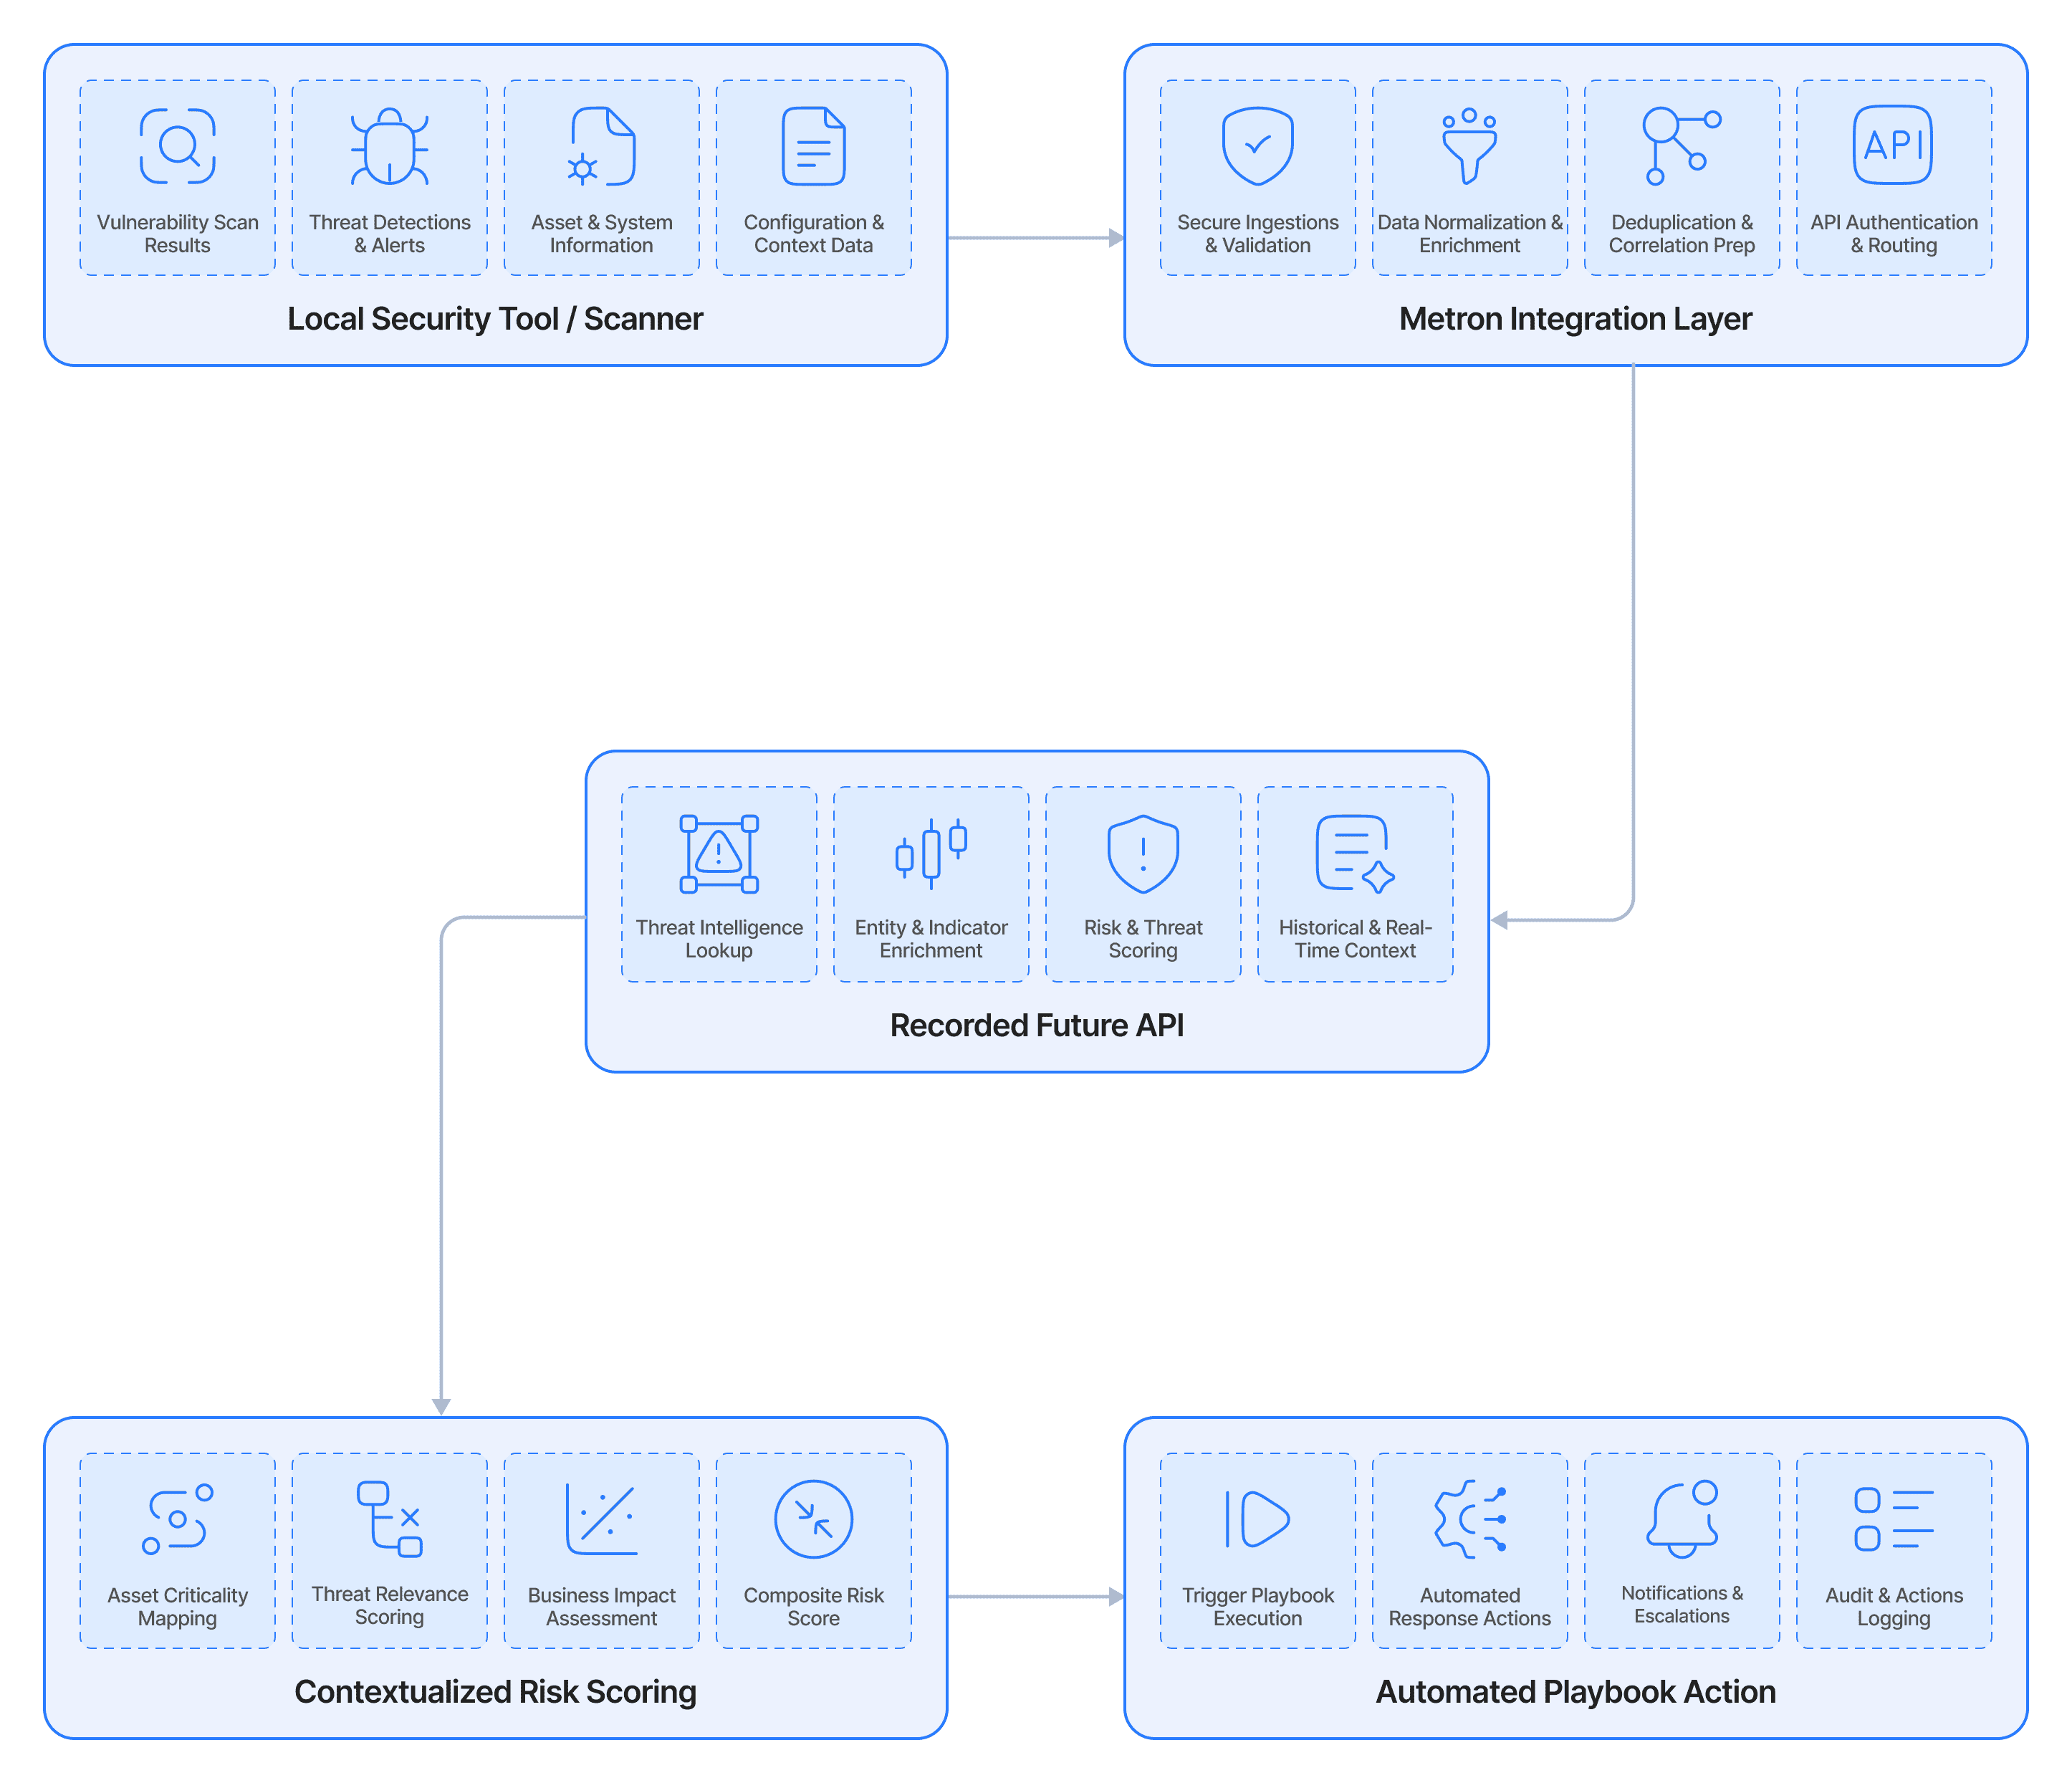
1. Flag Local Indicators: An internal security tool (like a SIEM or vulnerability scanner) captures a raw event log or generates a scan result.
2. Extract & Cleanse: The system normalizes the data format and matches it against current rules or open cases.
3. Query Enrichment APIs: We fire off low-latency, high-throughput calls to Recorded Future’s specialized Connect or SOAR APIs using secure access tokens.
4. Inject Live Context: The integration appends real-time risk scores, actor profiles, and specific threat traits back to the original security event.
5. Execute Automated Defence: The orchestration platform runs a designated playbook to isolate infected assets, update firewall rules, or bump high-risk vulnerabilities to the front of the patching line.
Recorded Future Integration Benefits
Events Ingest & Alerting
We stream high-fidelity Recorded Future alerts covering everything from leaked credentials and code repository exposures to domain typosquatting straight into your central operations dashboard.
IOC Enrichment
We power high-speed reputation lookups for IPs, domains, URLs, file hashes, and CVEs, overlaying real-time risk scores and historical context onto your raw security logs.
SOAR Actions & Playbooks
We trigger automated remediation playbooks inside your orchestration tools, allowing you to reset compromised corporate identities or detonate malicious files instantly.
Automatic Watch List Synchronization
We keep your active environments and Recorded Future Watch Lists perfectly in sync, removing the manual labour from asset monitoring.
Integration Use Cases
High-Throughput Bulk Enrichment
Manual IOC lookups slow down incident response. By connecting your workflow tools directly to Recorded Future's SOAR API, large batches of IPs, domains, and file hashes are enriched simultaneously, reducing mean time to resolve (MTTR) from hours to seconds.
Automated Playbook Remediation
Passive detections become immediate response actions. Incoming threat alerts, such as compromised credentials or lookalike domains, are translated into automated playbook commands that trigger platforms like Okta or Microsoft Identity to reset passwords and contain threats instantly.
Dynamic Watch List Automation
Asset risk is continuously updated by connecting vulnerability scanners such as Qualys or Tenable with Recorded Future Watch Lists. This helps security teams prioritize remediation based on active threats instead of relying solely on static severity scores.
Similar Connectors