Power Real-Time Security Operations with Devo
Overview
Devo is a cloud-native security data platform that analyzes and correlates security data in real time. By integrating Devo with cloud infrastructure, threat intelligence, SOAR, and ITSM platforms, we help unify security data, improve visibility, and automate incident response across the security ecosystem.
Key Products
Devo Cloud-Native SIEM
High-performance security information and event management built on HyperStream technology for real-time alerting, multi-tenancy, and sub-second query performance across months of hot data.
Devo SOAR
Autonomous orchestration and incident response engine that automates playbooks, triggers containment actions, and coordinates workflow execution across multi-vendor tools.
Devo DeepTrace
AI-driven autonomous threat hunting and investigation capabilities that automatically correlate events into complete attack stories and investigative timelines.
Devo Activeboards
Interactive real-time analytics and visualization dashboard engine to monitor SOC metrics, compliance postures, and high-velocity security data streams.
Devo Data Relay
Scalable on-premises and multi-cloud collector agent that ingests, tags, compresses, and securely routes high-volume syslog and local logs directly into Devo SaaS.
Devo Threat Intelligence Enrichment
Native context enrichment layer that dynamically correlates ingested events against live threat intelligence feeds and historical telemetry.
Devo Integration Architecture
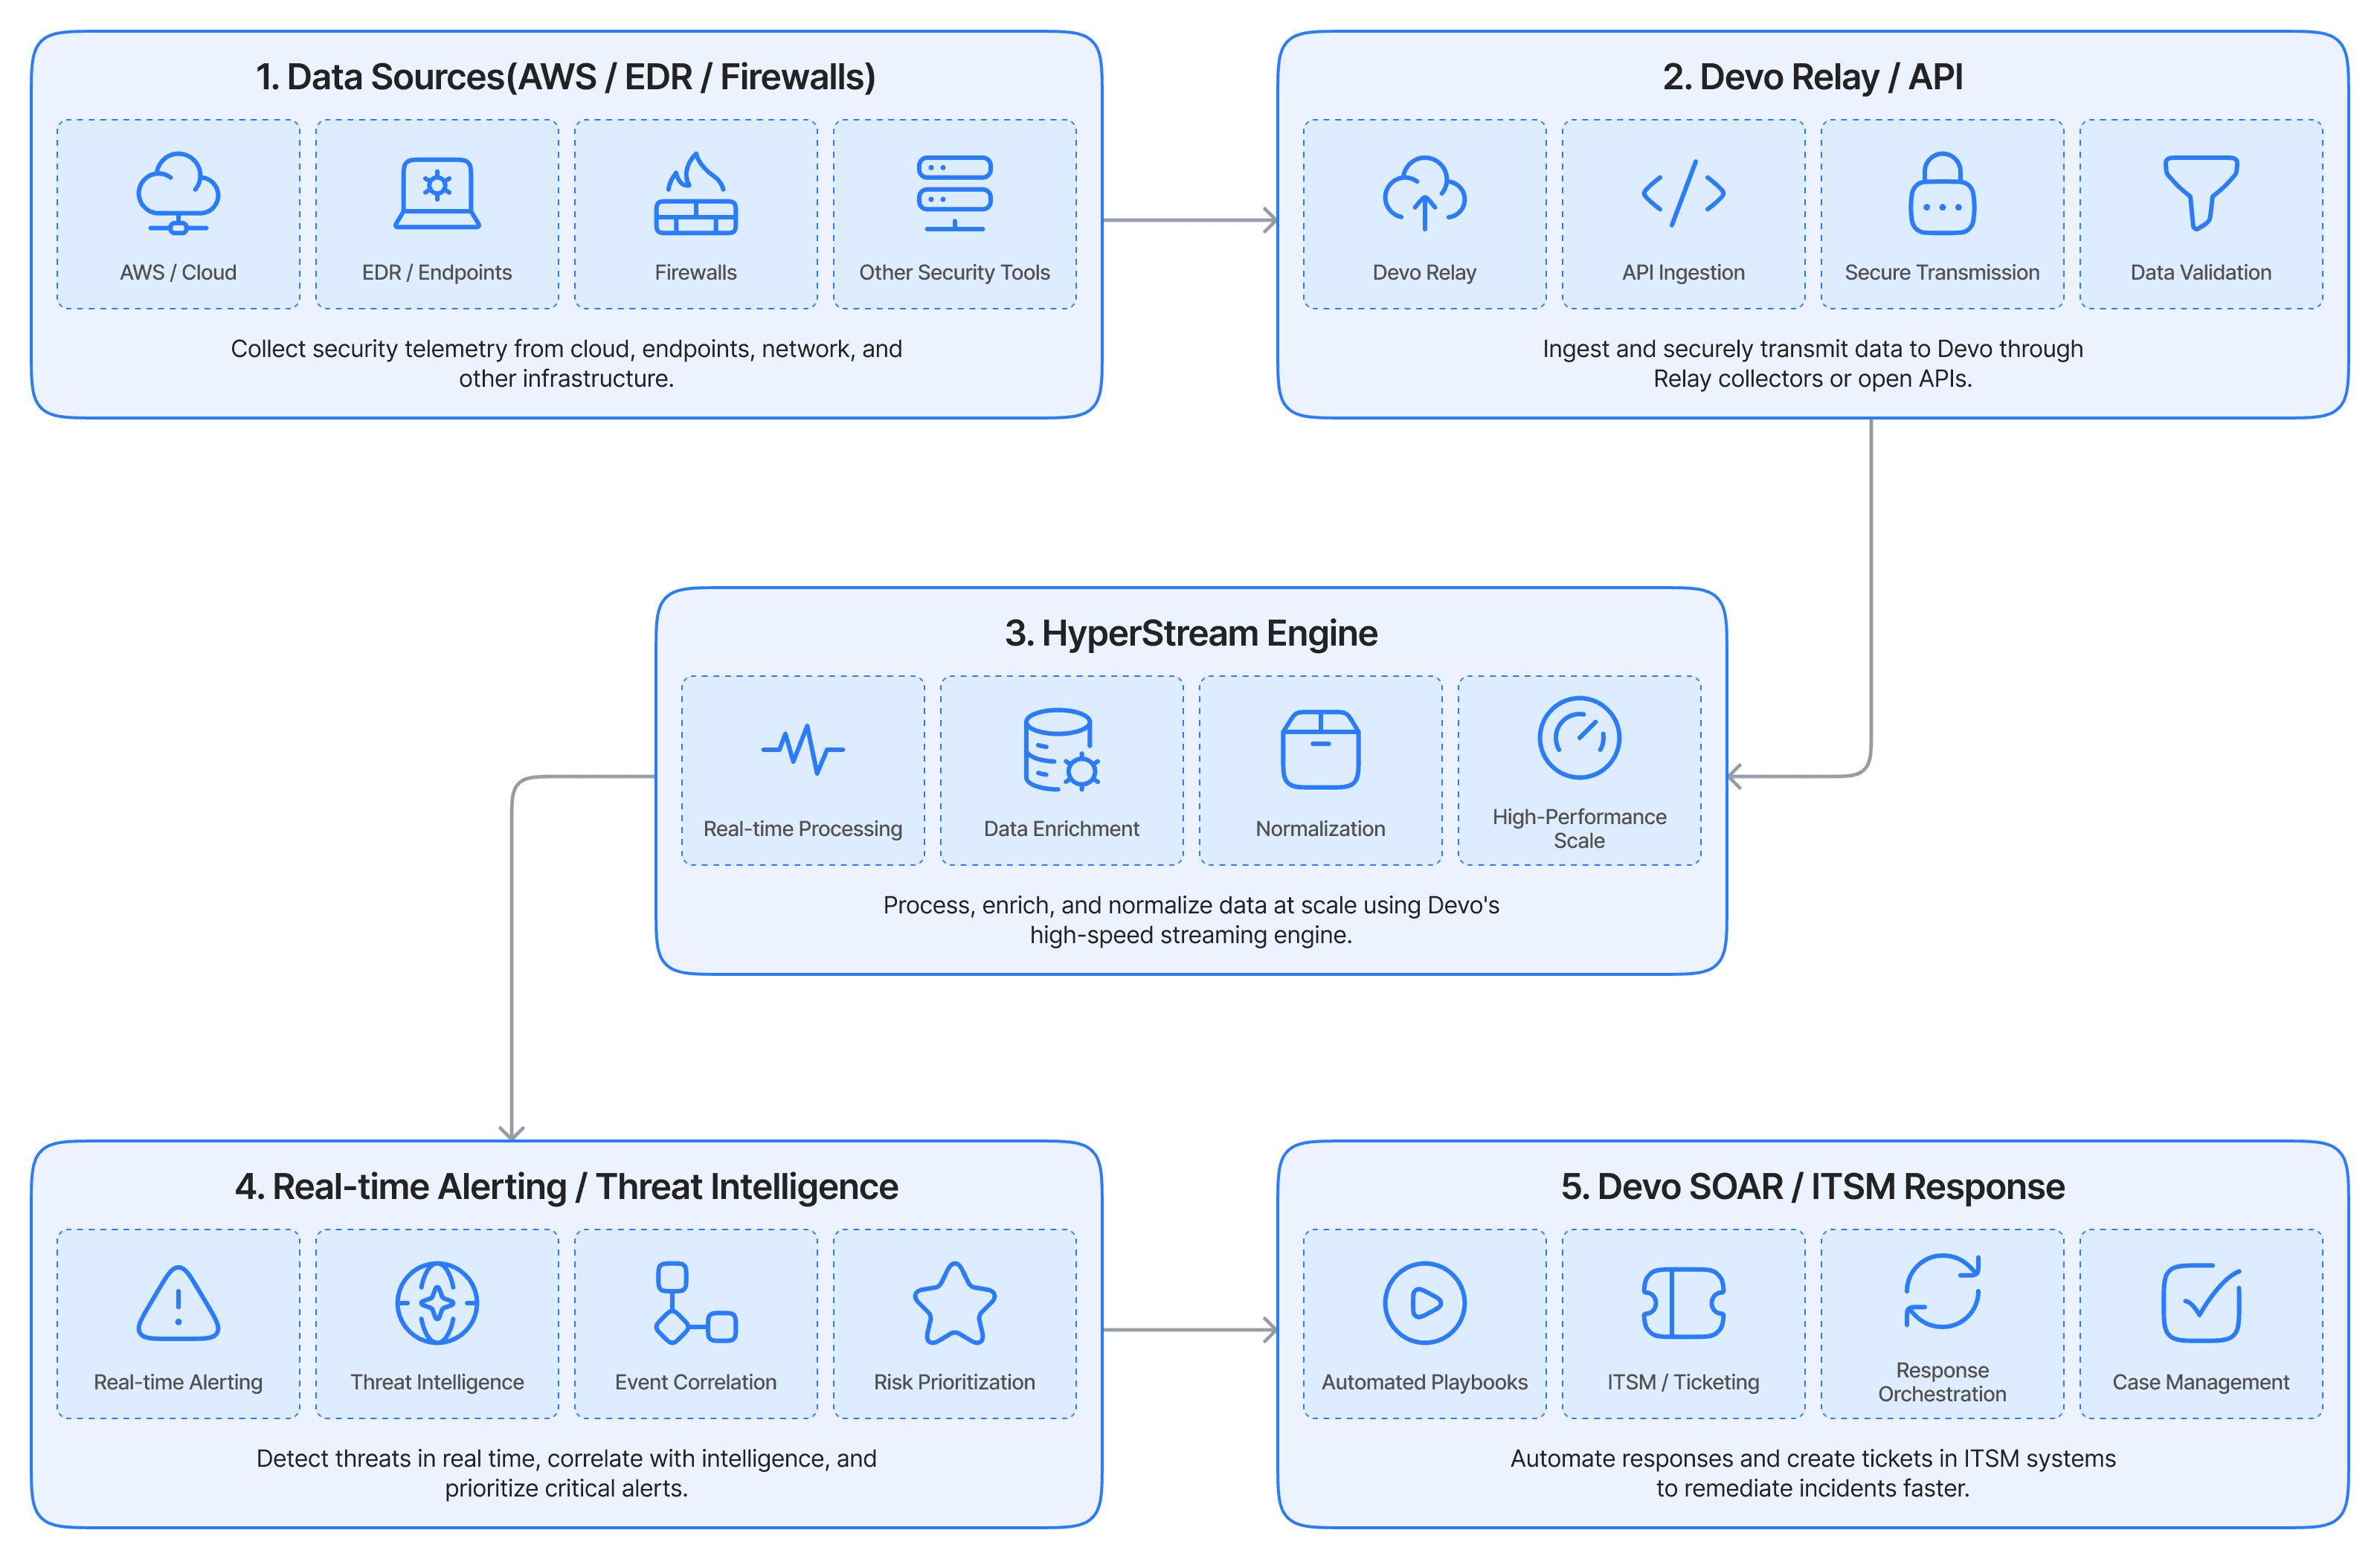
Raw telemetry (cloud logs, identity activity, network flows, and endpoint events) is pulled or pushed into Devo via secure Relays or HTTP APIs. The HyperStream engine normalizes and enriches the data with threat intelligence. When detections occur, alerts are pushed into Devo SOAR or external ITSM and EDR tools to run automated remediation steps.
Streamlined Logic
1. Telemetry Ingestion: Source platforms (e.g., CrowdStrike, AWS CloudTrail, Mimecast) send event logs to Devo Relays or direct REST endpoints via TLS-encrypted streams.
2. Parsing & Enrichment: Devo runs high-velocity parsers, tagging incoming records and appending context from threat intelligence feeds or CMDB assets.
3. Streaming Detection & Alerting: The HyperStream engine evaluates real-time rules against hot data streams without pre-indexing delays, firing alerts upon pattern matches.
4. SOAR & Case Triggering: Triggered alerts initiate automation playbooks within Devo SOAR or export webhooks to external security tools.
5. Automated Response: The integration executes remediation commands (e.g., blocking malicious IPs, creating Jira/ServiceNow tickets, or revoking OAuth tokens).
Devo Integration Benefits
Devo Relay Agents (Syslog & Local Collector)
Secure relay instances deployed on-premises or across multi-cloud infrastructure to collect, encrypt, and push syslog and raw event streams to Devo over secured ports.
Devo Push API / HTTP Collector
Webhook and HTTPS endpoints designed to accept real-time push events, JSON payloads, and unstructured telemetry directly from cloud services.
Pre-Built Data Parsers & Schema-Free Ingestion
Flexible ingestion engine supporting over 2,000 pre-configured parsers that automatically structure logs into standard tables while retaining raw log fidelity.
Devo SOAR Integration Library
Webhook and API connectors built specifically for Devo SOAR playbooks, allowing bidirectional actions in external platforms.
Integration Use Cases
Automated Real-Time Threat Hunting
By integrating cloud infrastructure and endpoint logs with Devo, we automate real-time correlation across millions of events per second, catching lateral movement and suspicious access instantly.
Dynamic Threat Intelligence Enrichment
We connect external threat feeds and perimeter defenders to automatically enrich incoming telemetry, reducing false positives and giving analysts actionable context right when alerts fire.
Closed-Loop Incident Remediation
We link Devo SOAR with ticketing systems and EDR solutions, executing automated playbooks to quarantine compromised systems within seconds of alert detection.
Similar Connectors