Unify Application Delivery and Security with F5
Key Products
F5 BIG-IP
Hardware and software-defined Application Delivery Controllers (ADCs) that deliver robust load balancing, Web Application Firewall (WAF) protection, and network security.
F5 Distributed Cloud Services
SaaS-based platform delivering unified multi-cloud networking, API security, and bot management across hybrid edge architectures.
NGINX App Protect & Management Suite
Lightweight, high-performance web server, reverse proxy, and microservices security platform tailored for cloud-native Kubernetes environments.
F5 BIG-IP Access Policy Manager
Provides centralized access management and authentication for applications and users. It helps organizations enforce access policies, manage user sessions, and secure access to enterprise resources.
F5 BIG-IQ Central Management
Centralized management console that provides single-pane-of-glass orchestration, licensing, and monitoring across all BIG-IP instances.
F5 Distributed Cloud Bot Defense
Advanced machine-learning engine designed to detect and block malicious automated traffic and bot scrapers across API endpoints.
F5 Integration Architecture
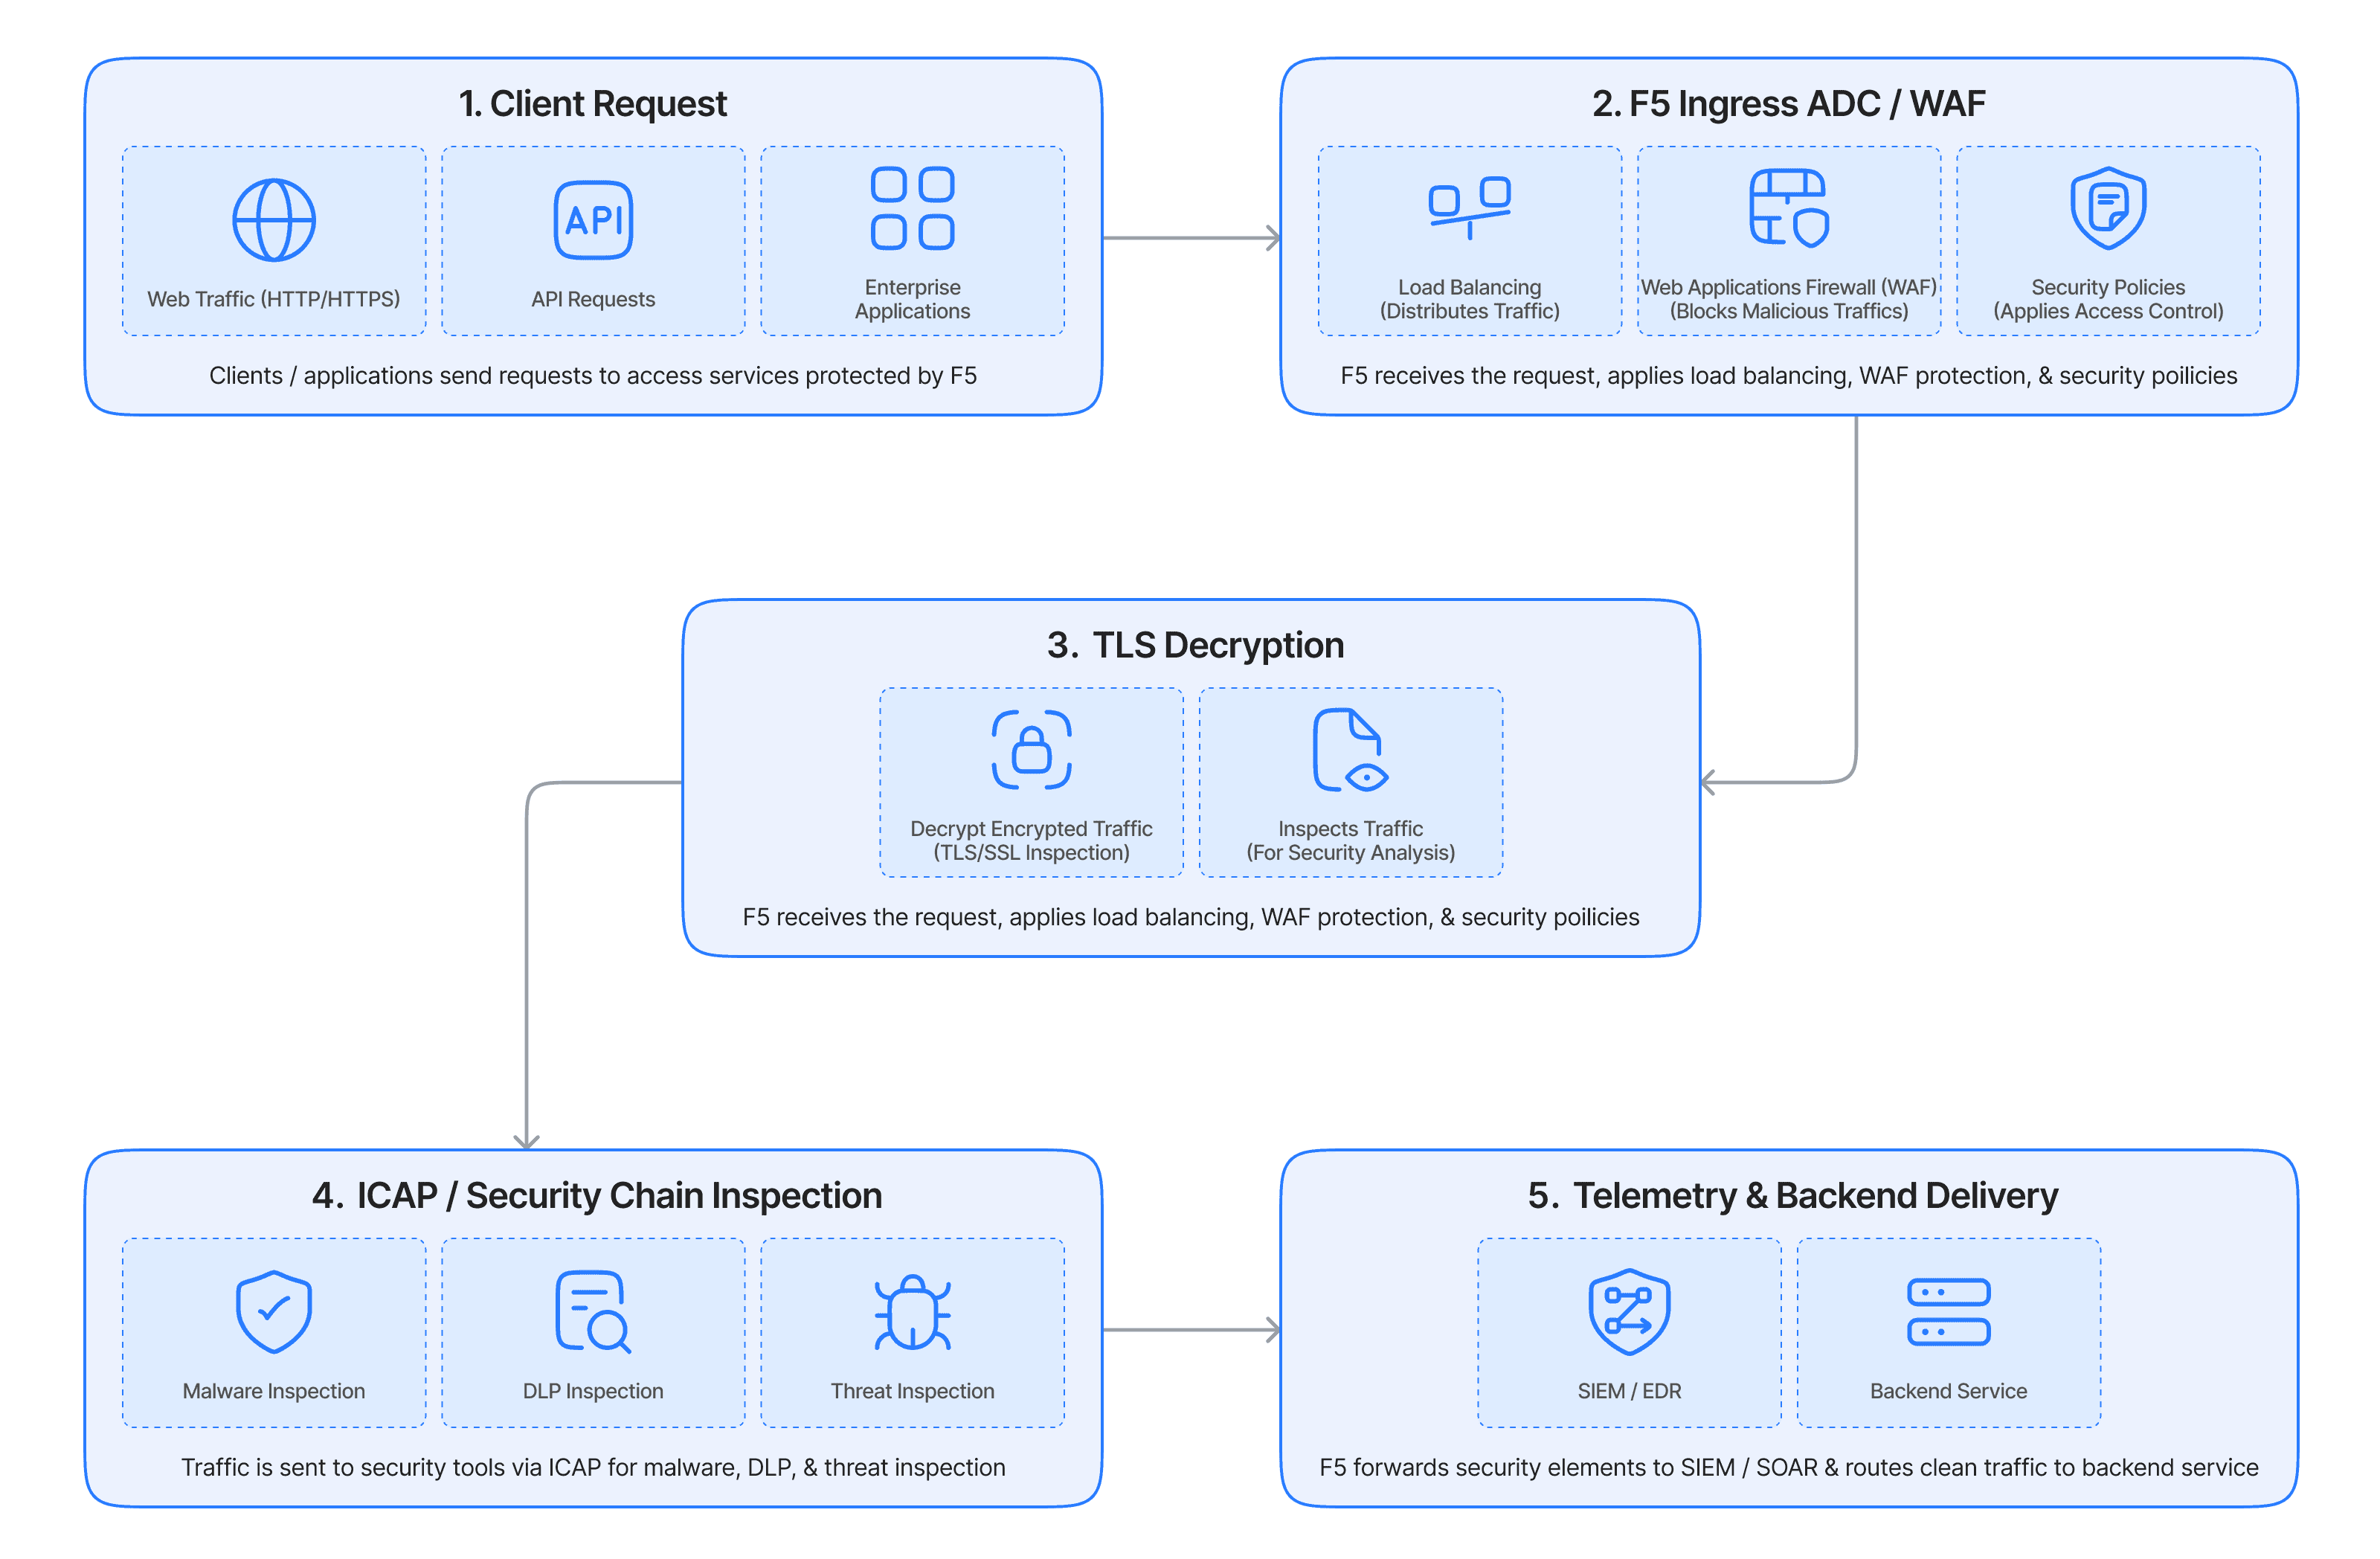
F5 manages application traffic through BIG-IP, providing load balancing, web application protection, and secure access controls. Incoming requests are evaluated against security policies and routed to backend applications. F5 also shares traffic logs and security events with external monitoring and security platforms through supported integrations.
Architecture
1. Traffic Ingestion & TLS Decryption: Inbound client requests land on the F5 Virtual Server, where SSL/TLS certificates terminate and decrypt the payload.
2. Dynamic Service Chaining: Decrypted payloads route via ICAP or dynamic service paths to integrated security solutions (e.g., OPSWAT, Symantec DLP) for threat scanning.
3. Telemetry & Log Ingestion: High-speed event telemetry (e.g., security alerts, WAF flags) streams in real time via REST APIs/HSL directly to SIEM and observability dashboards.
4. Policy Enforcement & Remediation: If threat telemetry triggers an alert, F5 automated playbooks update local IP blocklists, rate limits, or API schemas.
5. Egress Routing: Clean, optimized traffic passes down to backend application servers or cloud resources.
F5 Integration Benefits
Declarative REST & AS3 APIs
Programmatically configure and provision F5 application delivery services via JSON declarations using F5 Application Services 3 Extension (AS3) and REST APIs.
Infrastructure-as-Code (IaC)
Automate configuration management and deployment pipelines using pre-built Ansible collections, Terraform providers, and Cisco ACI app plugins.
ICAP & Security Service Chaining
Intercept and route decrypted HTTP/S payloads to third-party anti-malware, DLP, and threat-prevention engines using ICAP protocols and SSL Orchestrator dynamic service chaining.
Event Ingestion & Telemetry Connectors
Stream real-time traffic logs, security event data, and operational metrics directly into SIEM/SOAR platforms (e.g., Splunk, Datadog) via High-Speed Logging (HSL) and Telemetry Streaming extensions.
Integration Use Cases
Automated Infrastructure Provisioning
We streamline network operations by embedding F5 configuration into your existing CI/CD pipelines. Using Ansible collections and Terraform providers, apply web application firewall policies and issue TLS certificates automatically upon application deployment.
Dynamic Security Service Chaining
We eliminate security blind spots by decrypting enterprise traffic once and dynamically routing it across multiple security devices. Through integrations with tools like Cisco Firepower, Symantec DLP, and OPSWAT MetaDefender, traffic is inspected without creating network bottlenecks or latency.
Automated Certificate Lifecycle Management
We prevent application outages by pairing F5 appliances with modern machine identity platforms like DigiCert, Keyfactor, and Sectigo. Digital certificates auto-enroll, provision, and renew across your entire F5 ADC footprint without requiring manual human intervention.
Similar Connectors