Next-Level Security with XDR Integration
Security teams often manage disconnected tools across endpoints, identity, cloud workloads, networks, and automation platforms. This case study explores how XDR integrations bring these systems together to improve visibility, contextualize threats, and accelerate investigation and response.
In this case study, you’ll learn how to
1. Unify security data across endpoints, identities, networks, and cloud workloads
2. Integrate XDR, XSOAR, and IoT platforms for coordinated response
3. Add identity context to alerts through XDR and IAM integration
4. Reduce alert fatigue through enriched and prioritized detections
5. Automate investigations and response across connected security tools
Download the Case Study
Practical XDR Use Cases for Security Integrations
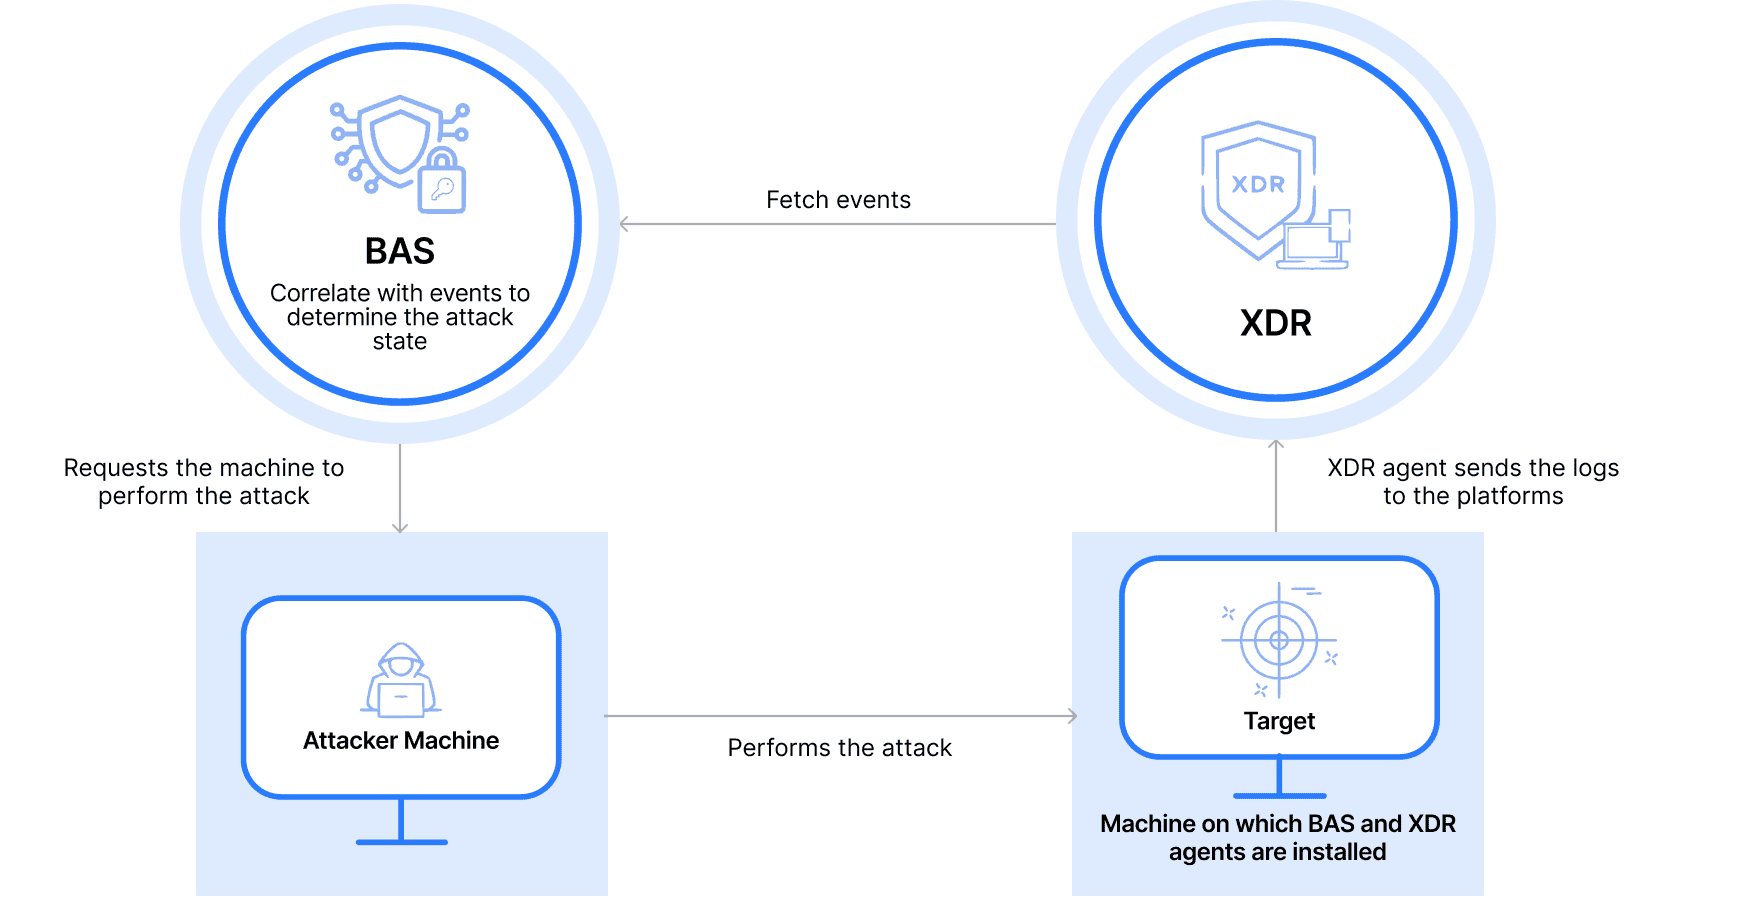
XDR + BAS Integration
To combine XDR with Breach and Attack Simulation platforms to continuously test security controls, identify detection gaps, and use simulated attack insights to improve threat detection and response readiness.
Similar Connectors